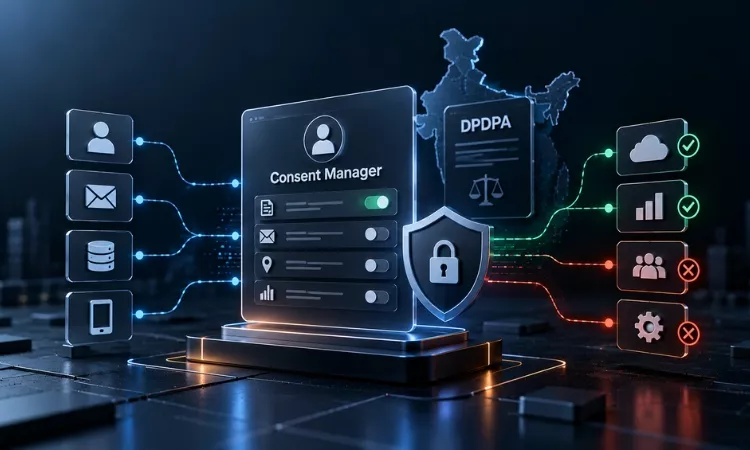
Consent now sits in hundreds of apps, portals and vendor forms, and most organizations cannot see or withdraw it from a single place. India’s Digital Personal Data Protection Act, 2023 (DPDPA) addresses this with a regulated intermediary, the Consent Manager.
For CISOs and governance leaders, the role moves consent out of individual checkboxes and into a managed, auditable record.
This article explains the statutory basis, the operating obligations under the DPDP Rules, 2025, and the steps enterprises should take before the framework takes effect.
What Is A Consent Manager?
A Consent Manager is an intermediary that the Data Protection Board of India registers. It gives individuals one place to grant, change, review and revoke permissions across several organizations. Section 2(g) defines the term, and Section 6(7) allows individuals to exercise consent through a registered Consent Manager.
The statute describes the Consent Manager as a registered person that serves as a “single point of contact” for individuals managing their consent. The Consent Manager answers to the individual rather than to the fiduciaries it serves. Each organization that decides why and how personal data is processed is a Data Fiduciary, and that role is distinct from the intermediary’s role.
Why Does The DPDPA Need Consent Managers?
Section 6 requires consent to be free, specific, informed, unconditional and unambiguous, given through a clear affirmative action. Section 6(4) requires withdrawal to be as easy as giving consent. Most consent programs struggle with that second requirement. An individual who has shared data with thirty services must contact each one separately, and each fiduciary stores the record in its own format.
A Consent Manager addresses that structural problem. It offers one interface for granting and withdrawing consent and one audit trail that records each decision with a timestamp and purpose. Law firm analysis of the framework, including the Consent Manager’s accountability to the individual, is available from AZB & Partners.
How Does A Consent Manager Work In Practice?
A Consent Manager onboards Data Fiduciaries, presents consent requests to individuals and records each grant, change and withdrawal. Part B of the First Schedule to the DPDP Rules, 2025 sets these operating obligations. The workflow follows five steps:
- Data Fiduciaries onboard to the platform and declare their processing purposes.
- The Data Principal receives a request that names the purpose and the data categories.
- The platform records the decision as a verifiable record.
- The individual reviews, modifies or withdraws consent through the platform’s website or app.
- The platform communicates withdrawals to the relevant fiduciaries so processing stops.
The Rules also require the data-sharing mechanism to prevent the Consent Manager from reading the content of the personal data it transmits. From a security standpoint, the architecture should separate consent metadata from payload data. A breach of the intermediary then exposes consent records but not the underlying personal data.
Who Can Become A Consent Manager And How Do They Register?
Under Rule 4(1) of the DPDP Rules, 2025, an applicant that satisfies the Part A conditions can seek registration from the Data Protection Board. The Board publishes the particulars and documents it requires on its website. The Ministry of Electronics and Information Technology publishes the Act and Rules, so confirm current registration conditions there before selecting a partner.
| Requirement | Source | Why It Matters to Enterprises |
| Company incorporated in India | Explanatory Note, DPDP Rules 2025 | Keeps enforcement reach within Indian jurisdiction. |
| Minimum net worth of ₹2 crore | Part A, First Schedule | Filters out under-capitalized operators holding sensitive consent records. |
| Interoperable platform meeting Board standards | Part A, First Schedule | Allows consent records to move between fiduciaries without custom integration. |
| Fiduciary capacity toward Data Principals | Part B, First Schedule | Aligns the intermediary’s duty with the individual. |
| No subcontracting of obligations | Part B, First Schedule | Prevents accountability from diluting across vendors. |
When Does Consent Manager Registration Take Effect?
Rule 4, which covers the registration framework, takes effect on 13 November 2026, one year after the Rules were notified. The core operational obligations, including consent notices, withdrawal mechanisms and audit logs, reach full compliance on 13 May 2027. Verify both dates against the official notifications before setting internal deadlines.
What Should CISOs Do To Prepare For Consent Manager Integration?
CISOs should map every consent collection point, assess gaps against the Part B obligations and build audit evidence before the registration window opens. The T-SAMA methodology from Ampcus Cyber gives the sequence:
- Train: Brief legal, privacy and engineering teams on how intermediary-managed consent differs from cookie banners.
- Scope: Inventory every system, vendor form and API that collects, stores or shares consent.
- Assess: Test current consent records against purpose limitation, withdrawal speed and the fiduciary duties in the Rules.
- Mitigate: Separate consent metadata from payload data in the architecture and define API contracts for withdrawal propagation. Vendor contracts are where withdrawal often breaks, so review third-party data risk in processor agreements.
- Audit: Collect evidence continuously, so a consent trail is ready when a regulator asks about one specific event.
What Are The Common Gaps In Consent Architecture?
The most common gaps are coarse consent records, manual withdrawal handling and weak visibility into processors. Privacy controls that map well to consent records are set out in ISO/IEC 27701, which extends ISO/IEC 27001 with privacy requirements.
How Is A Consent Manager Different From A Cookie Consent Banner?
A cookie banner is collected by one website for its own processing. A Consent Manager is an independent, registered intermediary that serves many fiduciaries and owes a duty to the individual. A banner answers whether one site may place cookies. A Consent Manager answers what an individual has allowed across all services and whether that permission can be changed in one place.
Do Data Fiduciaries Have To Use A Consent Manager?
No. The DPDPA does not require businesses to appoint a Consent Manager. Fiduciaries can still manage consent directly. Many organizations also misread the framework, and the common myths about the DPDP Rules are worth checking before any design decision. When a Data Principal chooses a registered Consent Manager, the fiduciary should be ready to honor the consent records and withdrawal signals that manager transmits.
What Should Organizations Do Next?
Organizations without an in-house privacy function can assign that work to a Data Protection Officer as a Service. Start with a purpose-to-system map, then test withdrawal end to end against real systems.
| Ready to test your consent architecture? Contact the Ampcus Cyber team for a DPDPA readiness review. |
People Also Ask
Is A Consent Manager Mandatory For Businesses?
How Is A Consent Manager Different From A Consent Management Platform?
Can A Consent Manager Read My Personal Data?
Does Using A Consent Manager Shift Compliance Responsibility Away From A Company?
What Happens If A Consent Manager Breaks The Rules?
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.