TL;DR
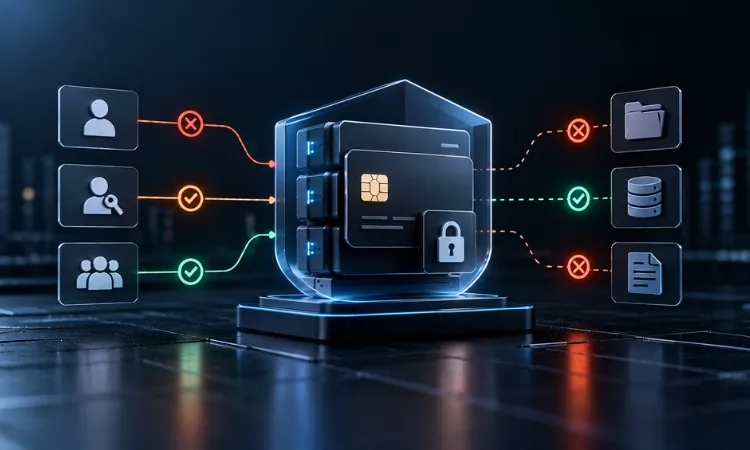
- PCI DSS Requirement 7 requires access to system components and cardholder data to be limited by business need to know, enforced through an access control system with a default deny-all setting.
- User accounts need documented approval and review at least every six months. Application and system accounts need least privilege and a risk-based review frequency.
- Assessors look for evidence that access was defined, approved, enforced, and reviewed, so keep role matrices, approvals, configurations, and sign-offs current.
PCI DSS Requirement 7 requires organizations to restrict access to system components and cardholder data by business need to know, so that only people and systems whose roles require access receive it. Need to know means access is granted for a defined job function, and least privilege means the access is limited to the minimum needed for that function.
The requirement is organized into three groups:
| Group | Focus |
| 7.1 | Processes and mechanisms for restricting access are defined and understood, with documented policies and assigned roles and responsibilities |
| 7.2 | Access to system components and data is appropriately defined and assigned, including the access control model, approvals, periodic reviews, and application and system accounts |
| 7.3 | Access is managed through an access control system that covers system components, enforces assigned permissions, and defaults to deny all |
Why Is Access Restriction Important for PCI DSS Compliance?
Access restriction limits how much damage a compromised account, an insider, or a vendor can cause. If an attacker obtains credentials, the data they can reach depends on the privileges attached to those credentials. Narrow privileges shrink that reach and make unusual activity easier to spot.
Requirement 7 also works alongside other requirements. It decides what access should exist, while Requirement 8 covers identifying users and authenticating them, and Requirement 10 covers logging and monitoring of access. Weak role definitions in Requirement 7 undermine both of the others, because strong authentication and detailed logs still protect excessive access. Reducing the amount of stored cardholder data also reduces the access you must govern.
While Requirement 7 is essential for PCI DSS compliance, we have also comprehensively covered Requirements 1 through 6.
How Should Organizations Implement PCI DSS Requirement 7?
Define roles and the access each role needs, assign access through an approval process, enforce it with an access control system, and review it on a schedule. A practical sequence follows:
- Document policies and assign owners for access restriction activities, which supports 7.1.
- Define an access control model based on job function and data needs, covering which resources each role may reach and at what privilege level (7.2.1).
- Assign access by job classification and function, using the least privilege necessary to perform job responsibilities (7.2.2).
- Require approval from authorized personnel for the privileges requested, and keep the approval record (7.2.3).
- Enforce permissions through an access control system that covers all system components and applies a default deny-all setting, so access is blocked unless explicitly allowed (7.3).
- Restrict user access to query repositories of stored cardholder data (7.2.6).
- Review all user accounts and related privileges at least every six months, confirm they remain appropriate, and obtain management acknowledgment (7.2.4).
- Manage application and system accounts to the same standard, as covered below.
How Do Application and System Accounts Fit Into PCI DSS Requirement 7?
Application and system accounts must have the least privileges necessary for the system or application to operate, and their access must be limited to the systems or processes that require them (7.2.5). These accounts include service accounts, scheduled jobs, integration credentials, and automation identities, which often carry broad rights because they were created quickly and never revisited.
Requirement 7.2.5.1 adds periodic review of this access at a frequency defined in the entity’s targeted risk analysis. The PCI Council recommends semi-annual reviews as a reference point, but the targeted risk analysis determines your actual frequency and must be documented. Both 7.2.5 and 7.2.5.1 were future-dated in v4.0 and are now mandatory. As automation and AI agents multiply machine identities, this area becomes harder to govern.
What Evidence Is Needed for PCI DSS Requirement 7?
Assessors expect to see that access decisions were defined, approved, enforced, and reviewed, and that the documentation matches what systems allow. Maintain these artifacts:
- Access control policy and documented roles and responsibilities for Requirement 7.
- A role-to-access matrix tied to job functions and cardholder data needs.
- Privilege approval records from authorized personnel.
- Access control system configurations showing enforcement and the default deny-all setting.
- Semi-annual user access review records with management sign-off.
- An inventory of application and system accounts, their privileges, and review records.
- The documented targeted risk analysis that sets your review frequency for those accounts.
The exact testing procedures belong to your assessor and the official standard, so confirm details against the current PCI DSS v4.0.1 documentation. Our PCI DSS v4.0.1 cheat sheet offers a quick reference.
What Are the Common Gaps in Access Restriction?
Most gaps come from access that was granted for a reason and never removed. Typical examples include:
- Role sprawl: Roles multiply until they no longer match job functions, and users hold permissions from earlier positions.
- Reviews without action: Access reviews take place on schedule, but reviewers approve everything, or no management acknowledgment is recorded.
- Unmanaged service accounts: Application and system accounts hold administrative rights, sit outside the user review process, and have no owner.
- Permissive defaults: Systems allow access unless blocked, which is the opposite of a deny-all setting.
- Shared and vendor access: Third parties retain standing access long after a project ends.
- Broad database access: Users can query repositories of stored cardholder data when their role does not require it.
As a hypothetical example, a payment application’s batch account created during implementation might still hold domain-level rights years later. Because it is not a person, it never appears in the user access review, yet it can reach cardholder data.
What Should Organizations Do Next?
Run a focused access assessment across your cardholder data environment, then fix the highest-risk entitlements first. Begin by inventorying all accounts, including service and vendor accounts, and mapping each to a business need. Remove access that cannot be justified, document the access control model, and schedule the first review cycle with named reviewers and a recorded sign-off. Then confirm that the access control system enforces deny-all and covers every in-scope component.
If your internal team lacks the capacity, Ampcus Cyber supports organizations through PCI DSS compliance services, including gap assessments, access model design, remediation guidance, and audit readiness, so that Requirement 7 evidence is in place before the assessment.
Conclusion
PCI DSS Requirement 7 turns least privilege into a testable control. It asks organizations to define who needs access, approve and enforce it through an access control system with a default deny-all posture, and review it regularly, including for application and system accounts. With v4.0.1 as the active version and all future-dated requirements now mandatory, organizations that keep their role definitions, approvals, and review records current will find assessments more predictable and their cardholder data less exposed.
Ready to find out where your access controls fall short of Requirement 7?
| Book a PCI DSS access readiness assessment with Ampcus Cyber and get a prioritized remediation plan before your next audit. |
People Also Ask
What is PCI DSS Requirement 7?
PCI DSS Requirement 7 is the control that restricts access to system components and cardholder data by business need to know. It requires documented roles, an access control model, approval of privileges, regular reviews, and an access control system that defaults to deny all.
What does least privilege mean in PCI DSS?
Least privilege means each user, application, or system account receives only the access needed to perform its defined function. In PCI DSS, this applies to people and to application and system accounts, and access should be assigned by job classification and function.
How often must user access be reviewed under PCI DSS?
Requirement 7.2.4 requires all user accounts and related access privileges to be reviewed at least once every six months. The review must confirm access remains appropriate and obtain management acknowledgment.
Do service accounts fall under PCI DSS Requirement 7?
Yes. Requirement 7.2.5 covers application and system accounts, which must have only the least privileges needed. Requirement 7.2.5.1 requires periodic review at a frequency set by the entity’s targeted risk analysis.
What is the difference between PCI DSS Requirement 7 and Requirement 8?
Requirement 7 decides what access should exist, based on business need to know. Requirement 8 covers identifying users and authenticating them. Both are needed, since strong authentication still protects excessive access if roles are poorly defined.
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.