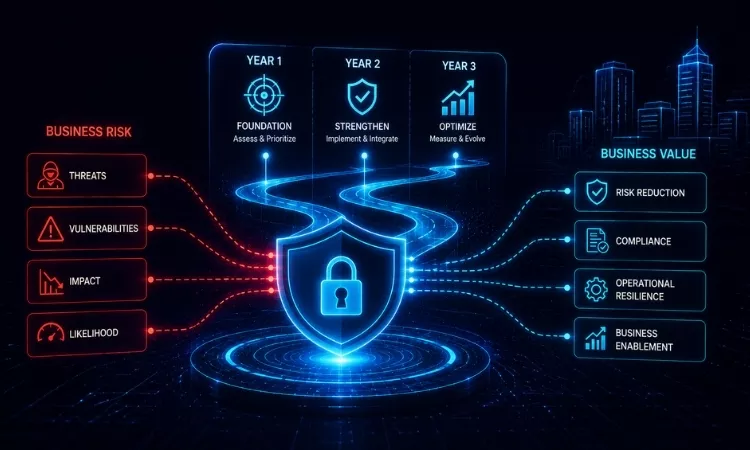
Cyber Risk vs Business Risk explains the critical difference between identifying a cybersecurity threat and understanding its potential business consequences. While cyber risk focuses on vulnerabilities, threat exposure, attack likelihood, exploitability, asset exposure, security control gaps, and threat severity, business risk translates those security concerns into outcomes such as financial loss, revenue disruption, operational downtime, customer impact, regulatory consequences, reputational damage, and strategic disruption.
The infographic also highlights four ways cyber risk becomes business risk: Financial, Operational, Regulatory, and Strategic. A cyber incident can lead to fraud, recovery costs, and lost revenue; system compromise can cause downtime and productivity loss; data exposure can trigger investigations, fines, and compliance obligations; and critical compromise can affect growth, customers, and competitive position.
For organizations asking “What is the difference between cyber risk and business risk?”, “How does cybersecurity risk affect business?”, or “How can cyber risk be translated into business impact?”, this visual provides a concise reference for connecting security findings with enterprise-level consequences.
Enjoyed reading this infographics? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.