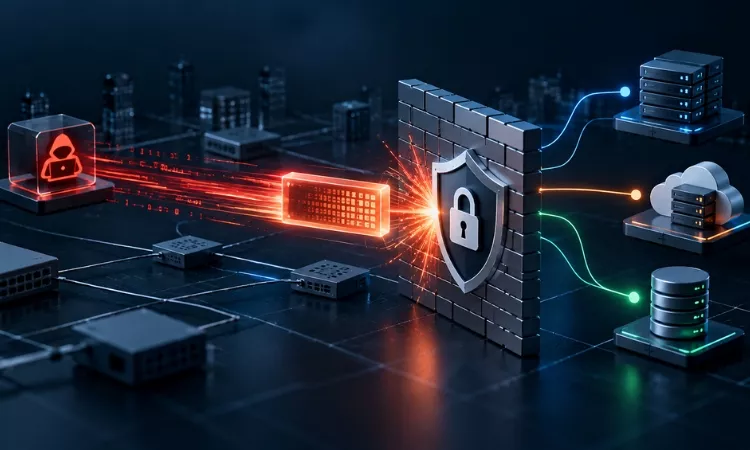
A single packet attack uses a specially crafted network packet to exploit weaknesses in how a system processes network traffic. Unlike volumetric denial-of-service attacks that rely on overwhelming a target with large amounts of traffic, these attacks can cause disruption through malformed headers, unexpected packet structures, oversized data, fragmentation issues, or resource-intensive processing.
Single packet attacks are particularly relevant to organizations operating legacy systems, unpatched network infrastructure, embedded devices, and other systems with weaknesses in packet processing.
Understanding how these attacks work can help security teams strengthen packet filtering, network segmentation, patch management, and intrusion detection controls.
What Is a Single Packet Attack?
A single packet attack is a network-layer exploitation technique in which an attacker sends a specially crafted packet designed to trigger a vulnerability or consume excessive system resources.
The packet may contain malformed fields, unexpected protocol values, excessive headers, unusual fragmentation patterns, or data that exceeds what the receiving system expects. If the target does not properly validate or process the packet, the result can range from packet rejection and service degradation to a system crash or denial of service.
The term “single packet attack” is best understood as a technique rather than one standardized attack category. Different implementations can target different protocols and processing mechanisms, including ICMP, UDP, IPv4 fragmentation, and IPv6 extension headers.
The key characteristic is the low volume of traffic required to trigger the vulnerability. The attacker does not necessarily need a sustained traffic flood. Instead, the attack depends on the target’s response to a specific packet structure.
This makes single packet attacks different from traditional volumetric attacks, where the primary objective is to consume bandwidth, connection capacity, CPU, or other resources through traffic volume.
How Does a Single Packet Attack Work?
A typical attack follows a relatively simple sequence:
- Identify a vulnerable target: The attacker determines which system, application, network device, or protocol implementation may be susceptible to malformed packet processing.
- Craft the packet: The attacker constructs a packet containing unusual or invalid fields, excessive size, fragmentation characteristics, or protocol combinations.
- Deliver the packet: The packet is transmitted to the target through an accessible network path.
- Trigger packet processing: The vulnerable system attempts to parse, reassemble, forward, or otherwise process the packet.
- Cause the intended effect: Depending on the vulnerability, the system may crash, consume excessive resources, expose information, or become temporarily unavailable.
The outcome depends entirely on the underlying vulnerability. A malformed packet by itself does not automatically compromise a system. It becomes dangerous when the target has a weakness in its packet-processing logic or configuration.
What Are the Common Types of Single Packet Attacks?
Several network attack techniques can involve specially crafted packets. Common examples include the following.
ICMP-Based Attacks
ICMP is widely used for network diagnostics and error reporting. Because network devices and operating systems process ICMP messages in different ways, weaknesses in ICMP handling can potentially be exploited.
Attackers may manipulate ICMP message types, fields, sizes, or other packet characteristics to trigger unexpected behavior. ICMP-based attacks can target availability, routing behavior, or information exposure depending on the implementation and vulnerability involved.
Ping of Death
Ping of Death is a well-known historical denial-of-service technique involving oversized IP packets and fragmentation.
The original attack relied on vulnerabilities in systems that failed to properly handle the reassembly of an oversized IP datagram. When fragments were reconstructed, the resulting datagram could exceed the expected maximum size and trigger memory corruption or a system crash.
An important distinction is that the original Ping of Death attack was associated with a malicious oversized datagram that could be transmitted through multiple IP fragments. Therefore, describing it simply as “one packet on the wire” can be misleading.
Modern operating systems generally include protections against the original vulnerability by validating packet lengths during fragmentation and reassembly.
Oversized ICMP Packets
Large or abnormal ICMP packets can also be used to test or exploit weaknesses in packet-processing implementations.
Modern systems generally reject packets that violate protocol or implementation limits. However, outdated software, embedded devices, and vulnerable network appliances may still require additional protection.
Malformed UDP Packets
UDP has a relatively simple header structure, but vulnerabilities can exist in the software that processes UDP traffic.
A specially crafted UDP packet may exploit weaknesses in input validation, memory handling, parsing, or application-layer processing. The resulting impact depends on the vulnerable implementation and may include a crash, service disruption, or other unintended behavior.
IPv6 Extension Header Attacks
IPv6 supports extension headers that provide additional information between the IPv6 header and upper-layer protocols.
An unusually long or complex chain of extension headers can increase processing requirements. Standards such as RFC 8883 define processing limits for cases including excessive extension headers, overly long extension-header chains, and oversized options.
An attacker may attempt to exploit systems that process these structures inefficiently, potentially causing resource exhaustion or degraded forwarding performance.
Malformed or Impossible IP Packets
Attackers can also construct packets containing inconsistent, invalid, or contradictory header information.
Examples may include invalid combinations of flags, unusual fragmentation values, invalid lengths, or other protocol inconsistencies. Security devices can use packet validation and protocol-aware filtering to identify and reject these packets.
How Do Single Packet Attacks Differ From DDoS Attacks?
Single packet attacks and DDoS attacks can both cause service disruption, but they rely on different mechanisms.
| Factor | Single Packet Attack | Volumetric DDoS |
| Primary mechanism | Exploits packet-processing weakness | Overwhelms resources with traffic volume |
| Traffic volume | Very low | Often extremely high |
| Main target | Vulnerable packet-processing logic | Bandwidth, connections, CPU, applications |
| Infrastructure required | Potentially minimal | Often requires distributed attack infrastructure |
| Detection | Requires packet-aware inspection | Traffic-volume and anomaly detection |
| Typical impact | Crash, resource exhaustion, or targeted disruption | Service degradation or widespread unavailability |
| Primary defense | Packet validation, patching, filtering | DDoS protection, traffic filtering, rate limiting |
The distinction matters because a security control designed primarily to identify traffic spikes may not detect a malicious packet that appears only once.
However, this does not mean single packet attacks automatically bypass modern firewalls. Modern security appliances can use protocol validation, signatures, malformed-packet detection, IPS rules, and other controls to identify suspicious traffic.
What Systems Are Vulnerable to Single Packet Attacks?
The greatest risk generally exists where packet-processing vulnerabilities remain unpatched or where systems cannot be easily updated.
Potentially exposed environments include:
- Legacy operating systems
- Unsupported network devices
- Older routers and firewalls
- Embedded devices
- Industrial control systems
- Medical and specialized equipment
- Internet-facing applications with vulnerable network components
- Systems with outdated firmware
- Devices with limited patching capabilities
Modern operating systems and network devices have addressed many historical packet-processing vulnerabilities through improved input validation, memory protections, fragmentation controls, and protocol-processing safeguards.
However, a modern operating system does not eliminate risk if the system is running vulnerable software, outdated firmware, or an exposed application with its own packet-processing weakness.
Legacy infrastructure deserves particular attention because organizations may continue operating systems and devices that cannot receive current security updates.
How Can Organizations Detect Single Packet Attacks?
Detection requires more than monitoring traffic volume. Security teams should combine packet inspection with endpoint, network, and infrastructure telemetry.
Signature-Based Detection:
Intrusion prevention systems, firewalls, and other network security controls can use signatures to identify known malformed packet patterns.
When a packet matches a known attack signature, the security device may log, drop, or block it depending on the configured policy.
Protocol and Packet Validation:
Security controls can inspect packet headers, lengths, fragmentation information, flags, extension headers, and other protocol fields.
Packets that violate expected protocol behavior can be rejected before they reach vulnerable internal systems.
Anomaly Detection:
Security teams can look for unusual packet characteristics or patterns that deviate from normal traffic.
Relevant indicators may include:
- Unexpected fragmentation
- Abnormal packet sizes
- Invalid header combinations
- Excessive IPv6 extension headers
- Unusual protocol behavior
- Repeated malformed packets
- Unexpected traffic directed toward legacy systems
Network and System Telemetry:
A successful packet-processing exploit may leave operational indicators even when the malicious packet itself is difficult to identify.
Security teams should correlate network events with:
- Unexpected system crashes
- Network device reboots
- Sudden service interruptions
- Application failures
- CPU or memory spikes
- Unusual device behavior
Perimeter security controls should also be positioned where they can inspect traffic before it reaches critical internal infrastructure.
Are Single Packet Attacks Still a Serious Threat?
The risk from many historical single packet vulnerabilities has decreased significantly because modern operating systems and network devices perform stronger input validation and packet-processing checks.
However, the underlying security issue remains relevant.
Organizations can still face risk when they operate:
- Unsupported systems
- Legacy network infrastructure
- Vulnerable embedded devices
- Specialized operational technology
- Outdated firmware
- Applications with insecure network parsing
- Systems exposed directly to untrusted networks
The broader lesson is important: low-volume traffic does not automatically mean low risk.
A single malformed packet may have little effect on a properly hardened system, while the same packet could cause a vulnerable device to crash or exhaust resources.
Security teams should therefore evaluate packet-processing vulnerabilities as part of broader network security assessments, vulnerability management, and penetration testing programs.
Ampcus Cyber provides network security assessments, vulnerability assessments, penetration testing, firewall configuration reviews, and security testing designed to identify weaknesses across enterprise infrastructure.
| Assess your network security posture before a malformed packet becomes a business disruption. Get a consultation with our experts. |
People Also Ask
What is the difference between a single packet attack and a buffer overflow?
A buffer overflow is a vulnerability or memory-safety condition that occurs when software writes more data to a memory buffer than it can safely hold. A single packet attack can be one way of triggering such a vulnerability by delivering specially crafted network input.
Can a single packet attack bypass a modern firewall?
Not necessarily. Modern firewalls and intrusion prevention systems can identify many known malformed packet patterns and protocol violations. However, protection depends on the specific vulnerability, device capabilities, configuration, and availability of detection signatures.
How does a Ping of Death attack work?
The historical Ping of Death technique exploited systems that failed to properly handle oversized IP datagrams during fragmentation and reassembly. When vulnerable systems reconstructed the malicious datagram, memory corruption could cause the system to crash. Modern systems generally validate packet sizes during reassembly and protect against the original vulnerability.
Should organizations disable ICMP to prevent single packet attacks?
No. Disabling ICMP across an entire network can interfere with legitimate network diagnostics and operational functions. A better approach is to apply appropriate filtering, validation, and rate-limiting policies while allowing required ICMP traffic.
Are single packet attacks a concern for cloud infrastructure?
Cloud environments benefit from modern infrastructure and security controls, but cloud-hosted workloads can still contain vulnerable applications, legacy components, or exposed network services. Organizations should therefore apply the same principles of patching, network segmentation, exposure reduction, and packet-aware monitoring to cloud environments.
How are single packet attacks related to network reconnaissance?
Some specially crafted network packets can be used to elicit responses that reveal information about network devices, protocols, or topology. Organizations can reduce unnecessary information exposure by controlling externally accessible services and monitoring unusual network probing activity.
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.