The Domain Name System (DNS) translates human-readable domain names into the IP addresses that computers use to connect. Every login page, payment gateway, email server and SaaS application your business depends on, starts with a DNS lookup.
DNS was designed in the 1980s for a trusted network. As a result, the original protocol has no built-in way to confirm that an answer is authentic. Attackers exploit that gap to send users and systems to servers they control, often without any visible warning.
This guide explains what DNS spoofing is and how the attack flow works. It also covers which defences security leaders should prioritize to protect users, data and brand trust.
What Is DNS Spoofing And How Does It Work?
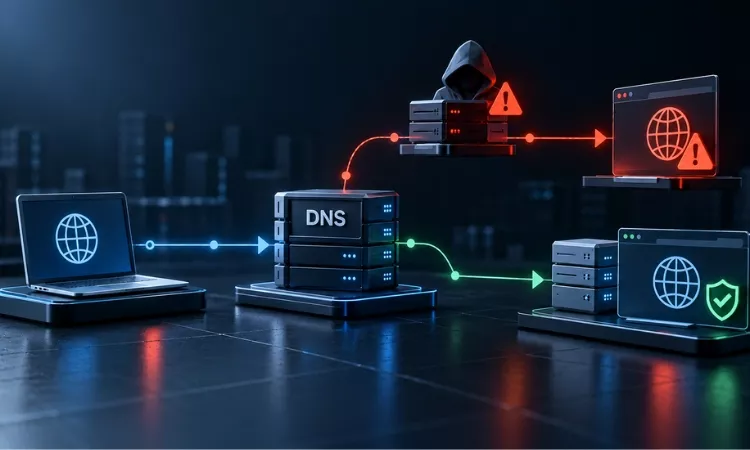
DNS spoofing is an attack in which a threat actor supplies false DNS records so that a domain name resolves to an IP address the attacker controls. The user types the correct web address, and the browser still connects to a malicious server.
DNS spoofing works because many DNS responses are accepted without cryptographic verification. A resolver that receives a forged answer can store it. It then serves that forged answer to every user who asks for the domain. The 2022 IDC Global DNS Threat Report found that 88% of organizations experienced DNS attacks, with an average of seven attacks per year. The same research put the average cost of a successful DNS attack at $942,000.
What Is The Difference Between DNS Spoofing, DNS Cache Poisoning And DNS Hijacking?
DNS spoofing is the broad goal of returning a false DNS answer. Attackers commonly reach that goal in one of two ways: DNS cache poisoning or DNS hijacking.
| Term | What the attacker does | Where it happens |
| DNS spoofing | Returns a forged DNS answer to redirect traffic | Any point in the lookup path |
| DNS cache poisoning | Injects false records into a resolver’s cache | Recursive DNS resolvers |
| DNS hijacking | Changes legitimate DNS records or settings | Registrar accounts, authoritative servers, routers or endpoints |
Cache poisoning affects everyone who uses the poisoned resolver until the record expires. DNS hijacking is often more damaging. In a hijack, the attacker changes the source record, so the false answer looks legitimate everywhere.
How Does A DNS Spoofing Attack Flow Work Step By Step?
A DNS spoofing attack moves from reconnaissance to redirection and then to data theft. Most real campaigns follow the pattern below.
- Target selection: The attacker identifies a high-value domain, such as a webmail portal, VPN gateway or payment page.
- Access or position: The attacker gains a foothold. Common routes include phishing a registrar account, compromising a home router and sitting on the same network as the victim.
- Record manipulation: The attacker alters a DNS record or injects a forged response so that the domain points to a malicious IP address.
- Redirection: Users and systems connect to an attacker-controlled server that imitates the real service.
- Exploitation: The attacker captures credentials, intercepts email, delivers malware or proxies traffic to stay hidden.
The Sea Turtle campaign shows this flow at nation-state scale. Cisco Talos reported that the group compromised at least 40 organizations across 13 countries. It changed name server records to redirect users to servers that harvested their credentials. The attackers also obtained valid TLS certificates, so victims saw a normal padlock in their browsers.
Why Is DNS Spoofing Dangerous For Enterprises?
DNS spoofing is dangerous because it turns trusted domains into delivery channels for phishing, malware and data interception. Users and security tools both tend to trust traffic that resolves to a known corporate or vendor domain.
The business impact of a successful attack usually falls into four areas:
- Credential theft: Fake login pages collect usernames, passwords and session tokens from employees and customers.
- Email interception: Altered MX records route corporate email through attacker infrastructure.
- Malware delivery: Software update servers or download portals redirect to malicious files.
- Brand and regulatory damage: Customers who lose data on a spoofed site still blame the legitimate brand.
In our network assessments, the most common weakness is a domain registrar account protected only by a password and shared across several administrators. That single account controls every public record the business owns.
How Can Organizations Detect DNS Spoofing?
Organizations detect DNS spoofing by monitoring DNS records, resolver behaviour and certificate activity for changes they did not authorize. Detection works best when DNS telemetry flows into the same tools analysts use for other security events.
Effective detection practices for enterprise security teams include:
- Comparing public DNS records against an approved baseline on a regular schedule.
- Logging recursive resolver queries and sending them to a SIEM for correlation.
- Watching Certificate Transparency logs for certificates issued for your domains without approval.
- Alerting on unexpected changes to name server, MX or A records at the registrar.
- Flagging spikes in NXDOMAIN responses or traffic to newly registered look-alike domains.
Continuous security monitoring makes these signals actionable, because analysts see DNS anomalies alongside identity and endpoint alerts.
What Are The Best Defences Against DNS Spoofing?
The best defences against DNS spoofing fall into four groups: authenticated DNS, encrypted DNS transport, strong account security and hardened resolvers. No single control closes every attack path, so enterprises layer them together.
- Deploy DNSSEC: Sign your zones so that validating resolvers can reject forged answers.
- Encrypt DNS traffic: Use DNS over HTTPS (DoH) or DNS over TLS (DoT) to stop on-path tampering.
- Lock registrar accounts: Enable registrar and registry locks, enforce phishing-resistant MFA and limit who can change records.
- Harden resolvers: Patch DNS software, randomize source ports and restrict recursion to internal clients.
- Use protective DNS: Block resolution of known malicious and look-alike domains.
- Segment critical services: Apply network segmentation so that a compromised device cannot easily intercept other traffic.
Government guidance supports this layered approach to DNS protection. CISA Emergency Directive 19-01 gave US federal agencies four tasks:
- audit their DNS records
- change DNS account passwords
- add MFA to those accounts
- monitor Certificate Transparency logs
Those four steps remain a practical baseline for private enterprises today.
Who Is Responsible For DNS Security In An Enterprise?
Responsibility for DNS security is shared between IT infrastructure teams, the security team and external providers such as registrars and managed DNS services. IT teams usually run internal resolvers and authoritative zones. Security teams own monitoring, threat detection and incident response for DNS events.
Gaps appear when nobody owns the registrar account or the list of domains the business has registered over the years. CISOs should assign a named owner for every domain. They should also review registrar access quarterly and include DNS providers in third-party risk assessments.
| Protect every domain, resolver and user connection from DNS spoofing by booking a network security assessment with Ampcus Cyber. |
People Also Ask
Does HTTPS protect against DNS spoofing?
HTTPS reduces the risk because browsers warn users when a certificate does not match the domain. It does not fully stop DNS spoofing, since attackers can sometimes obtain valid certificates, as the Sea Turtle campaign showed.
Does DNSSEC prevent DNS spoofing?
DNSSEC prevents forged DNS answers from being accepted by resolvers that validate signatures. It does not protect against a hijacked registrar account, because the attacker can change the signed records at the source.
Can a VPN prevent DNS spoofing?
A VPN can reduce local DNS spoofing by sending DNS queries through an encrypted tunnel to a trusted resolver. It does not help if the VPN’s own resolver or the domain’s authoritative records are compromised.
How long does DNS cache poisoning last?
A poisoned record stays in a resolver’s cache until its time-to-live (TTL) expires or an administrator flushes the cache. Attackers often set long TTL values to extend the impact.
Is DNS spoofing illegal?
Yes, DNS spoofing is illegal in most countries when it is done without authorization. Laws such as the US Computer Fraud and Abuse Act and the UK Computer Misuse Act cover it. Authorized security testing under a signed agreement is the exception.
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.