A mid-sized financial services firm migrated its customer database to the cloud three years ago. The team implemented firewalls, endpoint detection, and cloud infrastructure tools. Yet during a routine compliance audit, they discovered personally identifiable information accessible to 47% more employees than authorized policies allowed. The infrastructure looked secure. The problem was the data itself, sitting in misconfigured buckets, overly permissioned databases, and SaaS applications no one fully inventoried. This scenario repeats across enterprises daily. Traditional security tools protect infrastructure, but they leave data risk invisible until damage is done.
This gap between infrastructure security and actual data exposure is precisely what Data Security Posture Management addresses.
What Is DSPM(Data Security Posture Management)?
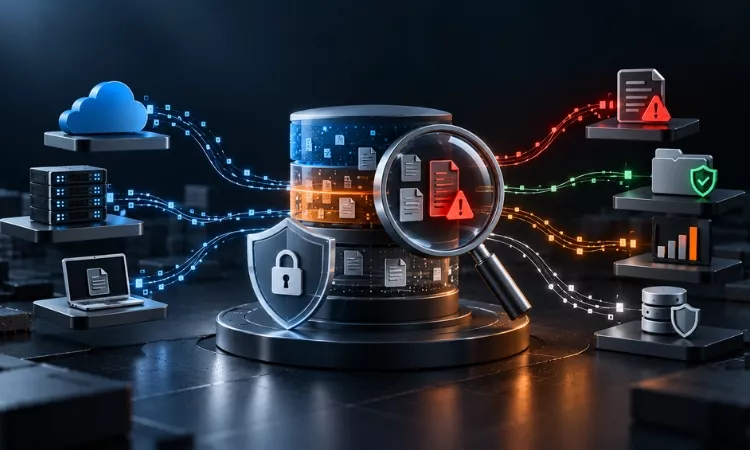
Data Security Posture Management is a modern security posture discipline that continuously discovers, classifies, and evaluates sensitive data across your entire environment while providing visibility into who can access it and whether it remains properly secured. Unlike tools that secure infrastructure or monitor data movement, DSPM focuses specifically on the data itself, treating data as your primary security perimeter.
Gartner introduced the term in 2022 as part of its Hype Cycle for Data Security, recognizing that organizations needed a fundamentally different approach to protect information in cloud-first, multi-environment landscapes. DSPM combines automated technologies with defined processes to answer the questions infrastructure-only tools cannot: Where does sensitive data live? Who can reach it? Is it exposed to unintended access? Which exposures create the most risk?
Why Does DSPM Matter For Modern Organizations?
Data sprawl has created an environment where cloud security teams cannot maintain manual visibility. Organizations operate across multiple cloud platforms, SaaS applications, on-premises systems, and increasingly, AI platforms. Each environment holds sensitive information like customer records, financial data, intellectual property, and health information scattered across thousands of repositories.
Consider the scale: A typical enterprise discovers between two to five times more sensitive data than it anticipated after implementing DSPM. Much of this data was invisible to security teams because it was never inventoried. Traditional data loss prevention focuses on preventing movement at network boundaries, but DSPM reveals data at rest and access patterns that DLP tools never see.
Without DSPM visibility, organizations cannot effectively manage risk because they do not know what they are protecting or who can access it. This creates three critical failures: regulatory compliance gaps, delayed incident response, and resource waste on low-priority security issues while critical data remains exposed.
How does DSPM work in practice?
DSPM platforms operate through four core stages that create continuous protection cycles.
Discovery And Inventory:
DSPM automatically scans cloud environments, SaaS platforms, databases, and data warehouses to identify all locations where data is stored. This goes beyond simple asset discovery, the tool also inventories what type of data exists in each location.
Classification And Context:
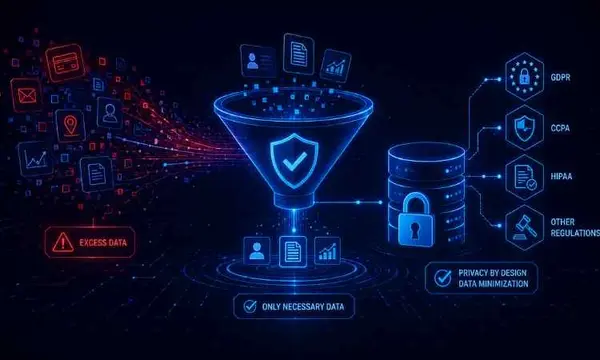
Once discovered, DSPM applies both automated classification and context. It identifies personally identifiable information, payment card data, health records, and proprietary information. More importantly, it understands regulatory scope, marking which datasets fall under GDPR, PCI DSS, HIPAA, or ISO 27001 requirements.
Risk Assessment And Access Analysis:
DSPM evaluates how each dataset is exposed. It examines encryption status, access permissions, public internet exposure, and whether overprovisioned users can reach sensitive information. This is where DSPM differs fundamentally from configuration tools, it cares about data protection, not just infrastructure misconfiguration.
Continuous Monitoring And Remediation:
DSPM does not conduct point-in-time scans. It maintains constant visibility as new data is created, access patterns change, and threats emerge. When issues are detected, the tool prioritizes remediation based on data sensitivity and business context.
What are the key components of DSPM?
Effective DSPM solutions include several interconnected capabilities. Data discovery engines map all repositories across cloud, on-premises, and SaaS environments. Classification modules apply both pattern-based rules and machine learning to tag sensitive data. Access analysis connects identity and access management systems to data permissions, revealing who can reach what. Risk assessment weighs exposure against data sensitivity to guide prioritization. Compliance mapping connects findings to specific regulatory requirements so teams can demonstrate ongoing compliance. Reporting and dashboarding provides visibility to security, compliance, and business leaders.
These components work together, not independently. Classification without access analysis is incomplete. Risk scoring without compliance context does not answer audit requirements.
How does dspm differ from cspm and dlp?
Organizations often ask whether they need DSPM if they already use Cloud Security Posture Management or Data Loss Prevention. The answer is that these tools address different problems.
CSPM focuses on infrastructure security. It detects misconfigured cloud buckets, open security groups, and unencrypted volumes. CSPM answers whether your cloud infrastructure is properly configured. DSPM focuses on data protection and detects which sensitive datasets are exposed, who can access them, and what that exposure means for your organization. While a CSPM tool might flag a misconfigured S3 bucket, DSPM tells you whether that bucket contains customer financial records accessible to contractors, information that fundamentally changes remediation priority.
DLP solutions control data movement. They monitor emails, file transfers, and network traffic to prevent unauthorized data exfiltration. DLP answers what is leaving your environment. DSPM answers what is sitting unprotected inside your environment. Over-permissioned data in properly secured buckets is invisible to DLP because no one is moving it yet.
The most mature security programs use CSPM, DLP, and DSPM together. CSPM secures the container. DLP prevents escape. DSPM ensures you know what is inside and understand the consequences of exposure.
What are the primary benefits of implementing DSPM?
Organizations implementing DSPM report several measurable outcomes. Risk management improves significantly when teams understand which exposures threaten sensitive data versus which represent low-risk configuration drift. Compliance acceleration transforms quarterly audit scrambles into continuous, automated proof of compliance. Many organizations report reducing compliance audit time from weeks to days.
Operational efficiency increases when DSPM reduces alert fatigue. Instead of investigating hundreds of low-priority configuration findings, teams focus on exposures involving regulated data. Faster incident response becomes possible because teams can immediately scope what data was accessible during a compromise rather than spending days reconstructing access paths. Cost reduction follows as teams avoid unnecessary remediation and focus resources on genuine risk.
What compliance standards does DSPM support?
Enterprise DSPM deployments face predictable challenges. Scalability issues emerge when organizations have terabytes of data across hundreds of repositories. Processing volume initially overwhelms teams, making phased rollouts essential. False positives can transform DSPM into security noise if classification algorithms are not properly tuned. Integration complexity increases when DSPM must connect with identity systems, DLP tools, SIEMs, and custom applications.
Organizational alignment represents the biggest implementation challenge. DSPM requires collaboration between security, compliance, data governance, and application teams. Groups that often lack established working relationships. Skill gaps also surface, as many organizations lack experience interpreting DSPM findings and translating them into policy changes.
Successful implementations address these challenges through phased rollouts that show value early, executive sponsorship that enforces cross-functional collaboration, and clear playbooks that assign ownership for remediation.
When should organizations implement DSPM?
The immediate answer is: now. If your organization stores sensitive data in cloud security environments, SaaS platforms, or multi-cloud architectures, you have unmapped data risk. The only question is whether you address it proactively or after a compliance failure or breach reveals it.
Practically, the best time to start DSPM is when you have executive support and can dedicate resources for proper implementation. Organizations that delay often face higher costs as data volume grows and compliance requirements tighten.
Who should lead dspm programs?
DSPM programs require executive sponsorship because they demand collaboration across teams. Chief Information Security Officers typically own the program, but success requires partnership with Chief Information Officers, privacy officers, and compliance leaders. At operational levels, cloud security architects own tool implementation while governance teams drive policy enforcement.
Key Takeaway
Data Security Posture Management transforms invisible data risk into continuous visibility and control. Rather than hoping your infrastructure tools protect sensitive information, DSPM shows you exactly what data you have, where it lives, who can access it, and whether exposures align with business risk tolerance. In environments where data sprawl accelerates daily, DSPM is the difference between proactive security and reactive breach response.
Gain visibility into where sensitive data resides, who can access it, and where hidden exposures could create compliance or security risks.
Ready to gain complete visibility into your sensitive data exposure?
Ampcus Cyber helps enterprises implement DSPM programs that reduce risk, accelerate compliance, and transform how security teams prioritize protection efforts.
| Connect with Ampcus Cyber’s security specialists to assess your data security posture and build a more proactive approach to data protection. |
People Also Ask
Is DSPM required for compliance?
An AI kill switch is a control that lets authorized people stop or isolate an AI system quickly and safely when it behaves in unexpected or harmful ways.
How long does DSPM implementation take?
Initial discovery and classification typically takes four to eight weeks. Full program maturity, including policy development and remediation workflows, takes three to six months for most organizations. Phased approaches that start with highest-risk data can show value within weeks.
Can DSPM prevent data breaches?
DSPM itself does not prevent breaches, but it eliminates the conditions where breaches cause massive damage. By reducing unnecessary access and identifying exposures before attackers find them, DSPM reduces breach probability and limits damage scope when breaches do occur.
Does DSPM work with data in transit?
DSPM focuses primarily on data at rest. For data in motion, integration with DLP and CASB tools provides comprehensive coverage across all data states.
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.