A mid-sized digital payments company had 412 suppliers classified as “Medium Risk.” The risk report had followed the same methodology for two years, with limited challenge from the audit committee. Three weeks later, a file transfer provider on that list suffered a breach that exposed cardholder data. The vendor had completed its annual assessment and maintained a current SOC 2 report. However, the company had no visibility into compromised administrator credentials circulating on the dark web.
The incident exposed a critical weakness in the organization’s TPRM program: vendors were being assessed based on compliance evidence, not the potential business impact of their risk. A payment-data provider and an office catering vendor should not carry the same risk profile simply because both completed their assessments.
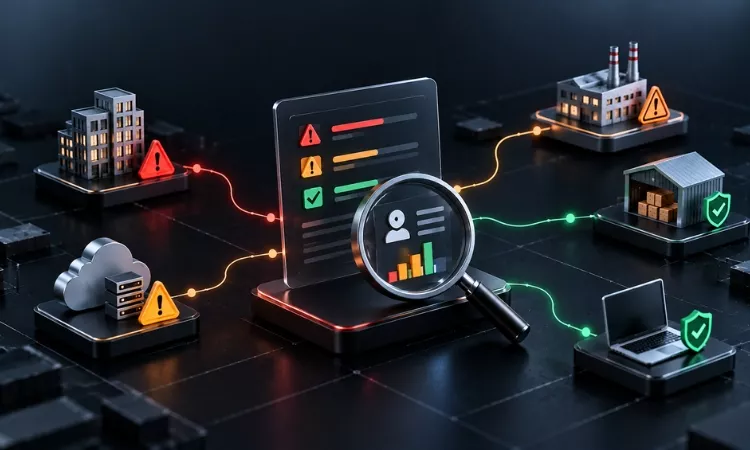
Vendor risk quantification changes the approach by connecting third-party risk to exposure, business impact, and potential loss. It gives risk teams a basis for prioritizing vendors based on the consequences they could create, rather than treating every “Medium” rating the same. That is the gap Wizard is designed to address.
What Is Vendor Risk Quantification In Third-Party Risk Management?
Vendor risk quantification is the process of converting third-party risk signals into a measurable score that shows which vendors pose the greatest threat to your business. It replaces subjective labels such as high, medium, and low with a consistent model that weighs likelihood and impact. The model combines what vendors report through questionnaires with what attackers can observe from the outside. It also accounts for how critical each vendor is to operations and what data it can reach.
Some organizations express the result as a numeric score, while others express it as potential financial loss. The output is a ranked vendor portfolio that security, procurement, and compliance teams can act on together. Our guide on modern TPRM risk scoring and automation explains how this scoring fits into the complete vendor lifecycle.
Why Do Traditional Vendor Risk Assessments Fail To Prioritize Risk?
Traditional vendor assessments fail because they depend on self-reported answers collected once a year, which leaves long blind spots between reviews. A questionnaire captures the controls a vendor claims on the day it responds. It cannot reveal a leaked credential, an exposed server, or a ransomware listing that appears three months later. Most programs also assess every vendor with equal depth, so analysts spend as much effort on a stationery supplier as on a cloud host. The exposure keeps growing, and Verizon’s 2025 Data Breach Investigations Report found that third-party involvement in breaches doubled to 30% in a single year. Across the TPRM programs our analysts support, the same three weaknesses appear repeatedly:
- Risk ratings go stale within weeks because nobody monitors vendors between assessment cycles.
- Evidence sits in email threads and shared drives, which slows every audit and renewal.
- Remediation requests lack owners and deadlines, so findings stay open for quarters.
How Is Vendor Risk Quantified And Scored?
Vendor risk is quantified by combining inherent risk, control effectiveness, and external threat exposure into one weighted score. Inherent risk reflects the data sensitivity, system access, and revenue dependency attached to each vendor. Control effectiveness reflects the evidence behind a vendor’s security program, including questionnaire responses, SOC 2 reports, ISO 27001 certificates, and policies.
External exposure reflects outside-in findings from attack surface scans, dark web monitoring, and email security checks. Mature programs also add financial health, ESG performance, and geopolitical exposure, since a vendor can disrupt your business without suffering a cyberattack. NIST SP 800-161 Rev. 1 supports this multi-factor approach by tying supplier assessment to enterprise risk tolerance.
How Does Wizard Help Prioritize Third-Party Risk?
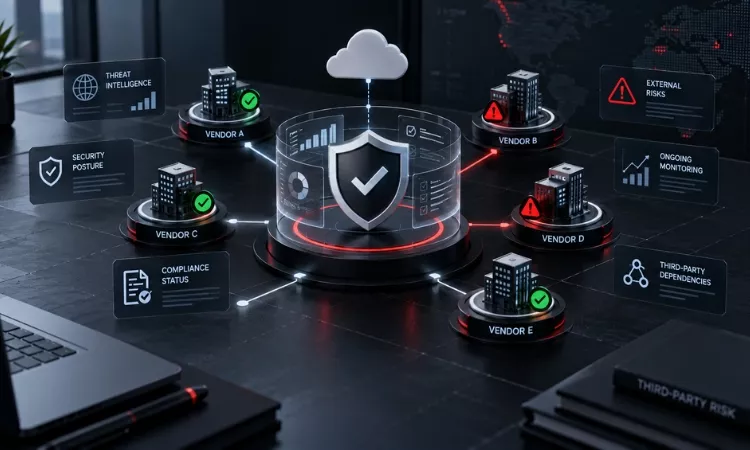
Wizard helps prioritize third-party risk by unifying questionnaires, digital exposure monitoring, financial health, ESG data, and continuous monitoring into a single risk score for every supplier. Many TPRM tools keep security ratings and questionnaire management in separate products, which forces teams to reconcile data manually. Wizard connects every signal to one supplier record, so analysts review a single view of each vendor.
- Automatic supplier tiering: Wizard tiers suppliers by compliance exposure and business relevance, so a cloud or network provider lands in Tier 1 while a logistics vendor lands in Tier 3. Teams can onboard suppliers from a pre-built list, through integration with an existing supplier platform, or by manual upload.
- AI-assisted questionnaires with citations: Wizard includes pre-built and custom templates that can be scheduled weekly, monthly, or quarterly. Its AI assistant searches supplier documents, drafts answers with source citations, and leaves a question blank when no evidence exists. After submission, reviewers flag risk factors and assign remediations directly from the response.
- Passive and active exposure scanning: Passive scans collect intelligence on leaked credentials, ransomware activity, infostealer logs, and email security posture through about 17,000 scripts and endpoints worldwide without contacting the supplier. With supplier consent, active scans simulate an attack to confirm exploitable vulnerabilities.
- Unified scoring and Dashboard AI: Wizard blends questionnaire and exposure findings into an overall risk score, and leaders can ask Dashboard AI questions such as “show the top 10 supplier risks.”
When Should Vendor Risk Scores Be Updated?
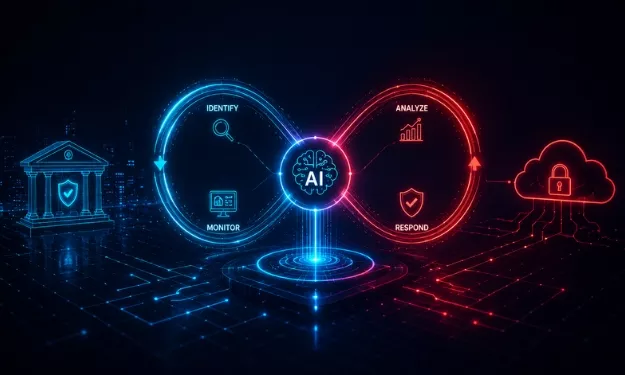
Vendor risk scores should update continuously, because a vendor’s risk changes the moment a breach, conflict, or disruption affects it. Wizard monitors cyber and geopolitical events in real time, including cyberattacks, natural disasters, wars, and regional protests, and maps each event to affected suppliers. Teams can then assign remediation tasks with defined SLAs and track each one to closure. Missed deadlines create a documented record that supports contract decisions. This visibility also helps teams estimate the vendor blast radius of a single supplier failure before it spreads.
Which TPRM Operating Model Fits Your Team, SaaS Or Managed Service?
The right model depends on your team’s capacity, since Wizard is available as self-managed SaaS or as a managed service with a dedicated Ampcus Cyber risk analyst. SaaS suits organizations with an established TPRM function that wants direct control over workflows and scoring. The managed service suits teams that lack analyst bandwidth or need to expand vendor coverage quickly. In the managed model, the analyst reviews supplier responses, validates findings, and drives remediation on your behalf. Organizations that want strategic program guidance can pair the platform with Ampcus Cyber’s third-party risk management services.
What Are The Best Practices For Implementing Vendor Risk Quantification?
The best practice is to define risk appetite first and then build scoring, tiering, and remediation around it. Programs that follow these five steps usually reach defensible prioritization within one assessment cycle:
- Agree on risk thresholds with leadership through a formal risk assessment before scoring any vendor.
- Tier vendors before assessing them so Tier 1 suppliers receive the deepest scrutiny.
- Validate questionnaire answers against outside-in exposure data.
- Assign every remediation item an accountable owner and a clear SLA.
- Report the top vendor risks to the board in operational and financial terms.
Turning Vendor Risk Into Decisions Your Board Can Trust
Vendor risk quantification gives CISOs and governance leaders a defensible answer to the question boards ask most often about suppliers, which is where the next breach is likely to come from. Wizard supports that answer with tiering, evidence-backed questionnaires, exposure intelligence, and continuous monitoring in one place. Teams move from counting completed questionnaires to reducing measurable risk. For organizations facing DPDP, PCI DSS, or DORA vendor oversight expectations, that shift also produces cleaner audit evidence.
| Find out which of your suppliers carry the most measurable risk and how to fix it fast by booking a Wizard demo with Ampcus Cyber. |
People Also Ask
Is vendor risk quantification the same as a vendor risk rating?
How often do third-party breaches happen?
What factors affect a vendor risk score?
Can AI fill out vendor security questionnaires accurately?
What is the first step in vendor risk management?
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.