GRACE, Ampcus Cyber’s GRC automation and continuous compliance platform, helps organizations manage controls, evidence, risk, and compliance requirements across multiple frameworks. The GRACE Crosswalk Report: From SOC 2 to ISO 27001 explores how organizations can reuse existing SOC 2 controls and evidence when pursuing ISO 27001:2022, instead of managing both frameworks as separate compliance programs.
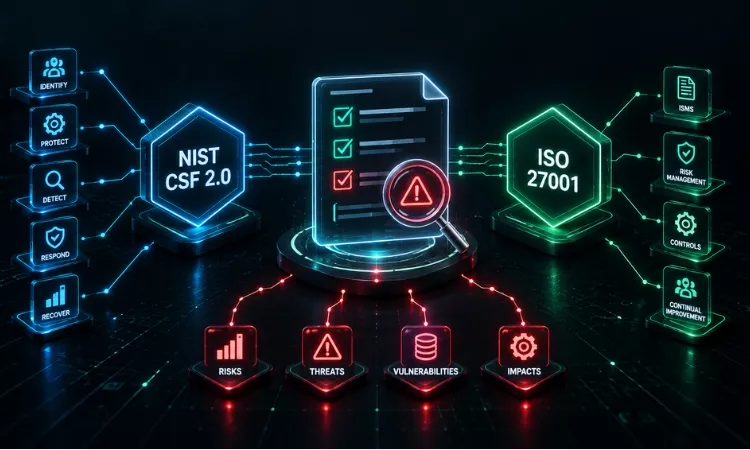
The whitepaper provides a practical SOC 2 to ISO 27001 crosswalk, showing where SOC 2 Common Criteria align with ISO 27001 Annex A controls and where genuine compliance gaps remain. It explains the critical differences between SOC 2 attestation and ISO 27001 certification, including the ISMS, Statement of Applicability, risk treatment, internal audit, and continual improvement requirements.
Security, compliance, GRC, and risk leaders will learn how to build a unified control inventory, map requirements across frameworks, reuse audit evidence, conduct targeted gap analysis, and move toward continuous compliance monitoring. The report also includes an implementation roadmap, measurement framework, strategic recommendations, and a composite SaaS example.
Download the report to understand what SOC 2 already covers, what ISO 27001 adds, and how cross-framework GRC automation can simplify dual compliance.