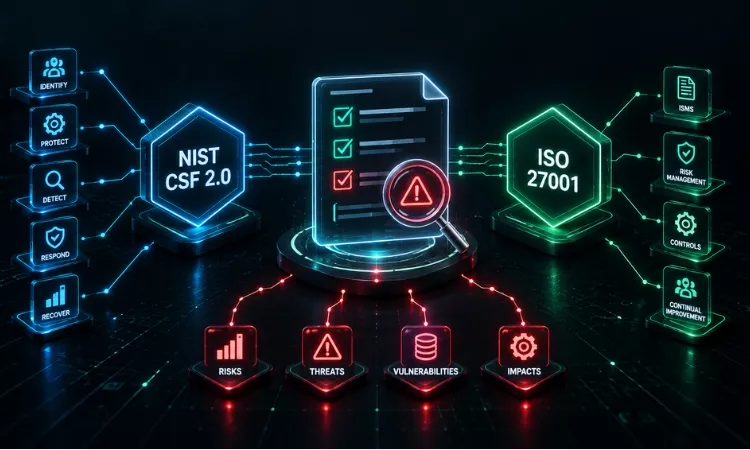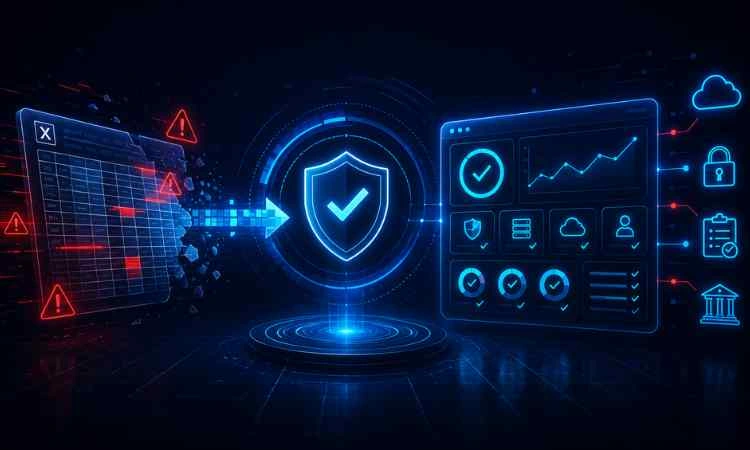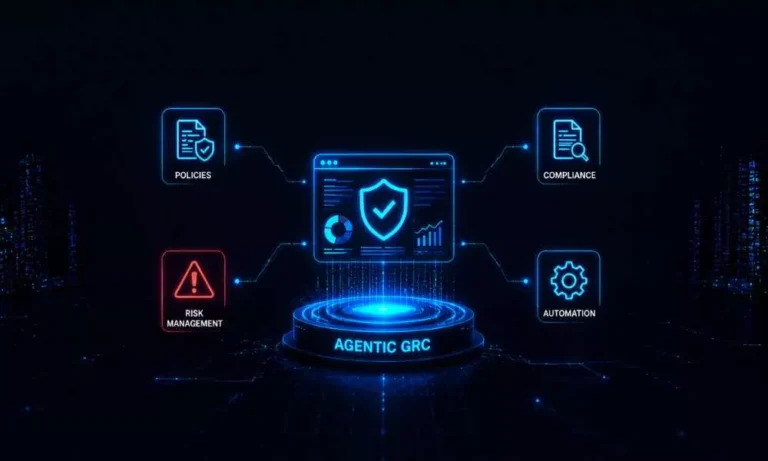
How is Governance, Risk, and Compliance (GRC) evolving from manual processes to intelligent, continuous compliance? This infographic explores the evolution of GRC from traditional, spreadsheet-driven compliance management to automation, intelligent GRC, and agentic compliance.
It explains how GRC automation reduces repetitive work through automated evidence collection, centralized workflows, control mapping, and compliance reporting. The next stage, intelligent GRC, uses AI to analyze risks, identify compliance gaps, connect controls, and provide actionable insights.
The infographic then introduces agentic compliance, where AI agents can continuously monitor regulatory changes, identify emerging risks, gather evidence, and recommend or initiate compliance actions. This represents a shift from simply automating GRC tasks to creating a more adaptive and continuously managed compliance environment.
The infographic also highlights GRACE, Ampcus Cyber’s Orchestrated compliance management software, which brings AI, risk, controls, evidence, and workflows together to help organizations manage compliance more efficiently and continuously.
Whether you are evaluating GRC automation, AI-powered compliance solutions, or the future of agentic GRC, this infographic provides a concise visual overview of how modern organizations are transforming their compliance operations.
Enjoyed reading this infographics? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.