TL;DR
- FedRAMP requires cloud service providers to implement a NIST SP 800-53 Rev 5 control baseline scaled to impact level, ranging from around 156 controls at Low to over 400 at High.
- Authorization comes through an independent 3PAO assessment, a documented System Security Plan, and a sponsoring federal agency, not through self-attestation.
- FedRAMP 20x, rolling out in phases since March 2025, is replacing static paperwork with continuous, machine-readable validation for organizations that qualify.
What Is FedRAMP?
FedRAMP, the Federal Risk and Authorization Management Program, is the U.S. government’s standardized process for assessing, authorizing, and monitoring the security of cloud services used by federal agencies. Any cloud service offering that processes, stores, or transmits federal data, whether infrastructure, platform, or software as a service, falls within its scope.
The program sits within the General Services Administration and now operates under statutory authority granted by the FedRAMP Authorization Act of 2022, replacing the policy memo that governed it for its first decade. Ampcus Cyber’s Compliance Compass work spans PCI DSS, ISO 27001, HITRUST, and CMMC, and FedRAMP follows the same logic: prove your controls work in practice, and paperwork alone will not satisfy an assessor.
What Security Controls Does FedRAMP Require?
FedRAMP requirements are built on the NIST SP 800-53 Rev 5 control catalog, tailored into baselines that scale with how sensitive the data is and how serious a breach would be.
- Low baseline: Around 156 controls, for systems handling public, non-sensitive information such as informational websites.
- Li-SaaS baseline: A lighter version of Low, for SaaS products that touch only minimal login data. Roughly 45 to 65 controls need full documentation and assessment, with additional controls covered by attestation.
- Moderate baseline: Around 325 controls, the level most providers pursue, covering systems where a breach would cause serious but not catastrophic harm.
- High baseline: Just over 400 controls, reserved for systems where a breach could threaten life, safety, or mission.
Each control sits in a family such as Access Control, Incident Response, or Configuration Management, drawn from the 20 control families in the full NIST SP 800-53 Rev 5 catalog.
How Does The FedRAMP Assessment Process Work?
The FedRAMP assessment process centers on independent verification, not self-reporting. A cloud service provider documents every control in a System Security Plan, then a Third-Party Assessment Organization tests whether those controls hold up in practice.
A 3PAO assessment typically includes documentation review, vulnerability scanning, interviews with system owners, and hands-on advanced penetration testing against the system boundary. The findings go into a Security Assessment Report, submitted with the SSP to the sponsoring agency. Any gap between what the SSP claims and what the 3PAO found becomes a line item in a Plan of Action and Milestones, tracked with an owner and a deadline until it closes.
None of this end at authorization. Providers submit monthly vulnerability scans, POA&M updates, and inventory changes, plus an annual reassessment. FedRAMP treats security as a condition that must keep holding, not a milestone reached once.
What Are The FedRAMP Authorization Paths?
Two paths lead to authorization today, and the choice affects both timeline and cost.
Agency Authorization
A federal agency sponsors the cloud service provider directly, reviews the SSP and SAR, and issues its own Authority to Operate. This is now the primary route into FedRAMP. Once granted, other agencies can reuse the same authorization through the FedRAMP Marketplace instead of starting a fresh review.
The Legacy Board Path
The Joint Authorization Board once issued government-wide provisional authorizations directly. That function now sits with the FedRAMP Board established by the 2022 Authorization Act, and centralized board-led reviews have become far less common as agency sponsorship and the new 20x path take over most new authorizations.
Providers targeting a defense-adjacent buyer should also expect CMMC to come up in the same conversation. It governs contractors handling controlled unclassified information and often travels alongside FedRAMP in defense procurement.
What Is Changing Under FedRAMP 20x?
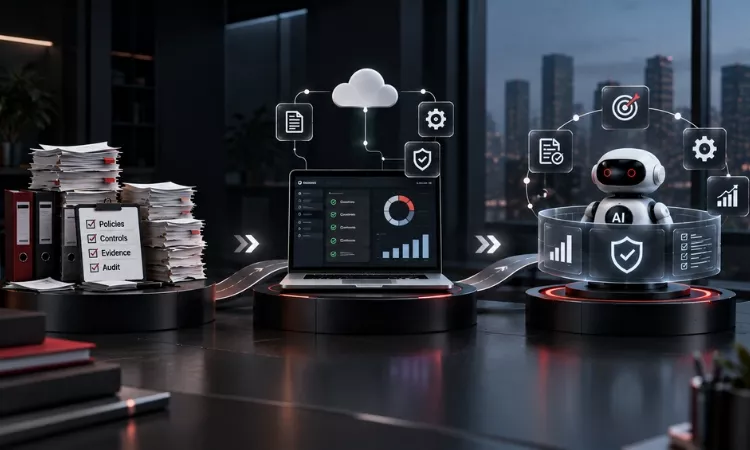
FedRAMP 20x is a new authorization path built on the 2022 Authorization Act and a 2024 OMB memorandum, designed to replace static documentation with continuous, machine-readable proof of security. Participants demonstrate a smaller set of Key Security Indicators and submit evidence in formats built for real-time validation rather than a one-time paperwork review. Ampcus Cyber’s take on this shift toward continuous, evidence-based assurance is laid out in our guide to ComplyX GRACE.
The rollout has moved in phases. A Low-impact pilot completed in September 2025, clearing the FedRAMP authorization backlog entirely. A Moderate-impact pilot followed in November 2025, and the program is now moving toward wide-scale adoption. The legacy Rev 5 process remains available, but the FedRAMP PMO has scaled back the guidance it once provided for it, so providers starting fresh today should evaluate the 20x path first.
What Are Best Practices For Achieving And Maintaining FedRAMP Authorization?
- Start with a readiness assessment: Map current controls against the target baseline before engaging a 3PAO, so the formal assessment confirms readiness instead of discovering gaps.
- Inherit controls where you can: Building on AWS GovCloud, Azure Government, or another already-authorized platform removes a share of physical and infrastructure controls from your scope.
- Treat documentation as a living system: An SSP that goes stale between reviews is the most common reason POA&M items pile up.
- Automate evidence collection early: Gathering monthly scans and inventory updates by hand does not scale. Platforms such as GRACE exist to keep evidence current across frameworks instead of rebuilding it every cycle.
- Budget for the assessment, not just the build: 3PAO engagements and annual reassessment are recurring costs, not one-time line items.
- Decide your path early: Evaluate whether FedRAMP 20x fits your system before defaulting to the traditional Rev 5 baseline, since the two paths require different evidence and timelines.
Weighing whether to pursue the traditional FedRAMP baseline or the new 20x path?
| Book a demo of GRACE, Ampcus Cyber’s continuous compliance platform, and see how evidence stays audit ready year round. |
People Also Ask:
How long does FedRAMP authorization take?
A traditional Agency Authorization typically takes six to eighteen months depending on baseline and readiness. FedRAMP 20x is designed to shorten that timeline for organizations that qualify.
What is a 3PAO?
A Third-Party Assessment Organization is an accredited, independent assessor that tests whether a cloud service provider’s implemented controls match its documentation, then reports results to the authorizing agency.
Is FedRAMP the same as CMMC?
No. FedRAMP authorizes cloud service offerings sold to federal agencies. CMMC certifies contractors that handle federal contract information or controlled unclassified information, most often in defense supply chains.
Does FedRAMP authorization expire?
Authorization has no fixed expiry date, but it depends on continuous monitoring and annual reassessment. Lapses in ConMon deliverables or unresolved POA&M items can put an authorization at risk.
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.