TL;DR
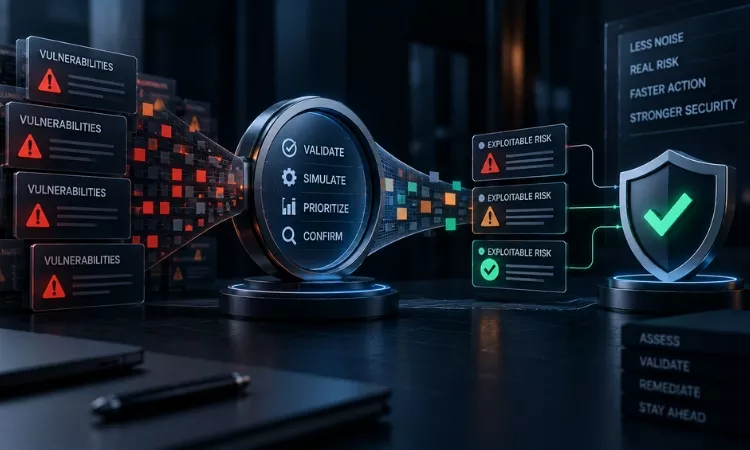
- Vulnerability management finds, scores, and tracks known weaknesses. Exposure validation tests whether those weaknesses, alone or chained together, can be exploited in your specific environment.
- Only about 6% of published CVEs have ever been observed under active exploitation, so severity scores alone routinely misdirect remediation effort.
- The strongest programs run both together: vulnerability management supplies the raw findings, exposure validation confirms which ones deserve immediate action, and mobilization closes the loop.
Explaining Vulnerability Management
Vulnerability management is the ongoing process of discovering, classifying, scoring, and tracking software and configuration weaknesses across an organization’s IT estate. It relies on scanners, asset inventories, and scoring systems such as CVSS to show what is present and how severe it looks on paper. A mature program runs on a cycle: scan, classify, patch, rescan.
It answers one question well: what weaknesses exist in our environment. It rarely answers the second, more important one: which of these weaknesses could someone outside the network use against us. Programs that stop at counting and patching CVEs, with no documented way to weigh business impact, tend to bury remediation teams in low-value work. Structured vulnerability remediation guidance keeps that queue focused on risk instead of volume.
Exposure Validation Defined
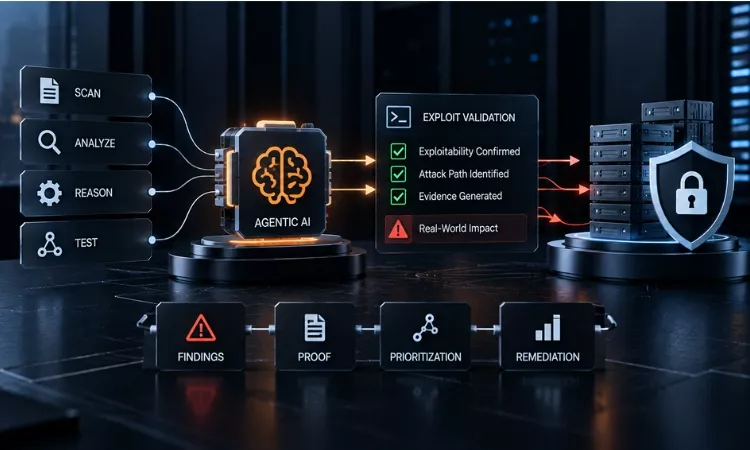
Exposure validation is the practice of testing whether a vulnerability, misconfiguration, or exposed asset can be exploited under real attack conditions, not just whether it shows up on a scan report. Instead of stopping at detection, validation attempts controlled exploitation, chains findings together the way an attacker would, and produces proof of impact.
It borrows the mindset of penetration testing and red teaming but runs on a tighter, often continuous cycle. The output is not another severity score. It is proof: this exact path, from this exact entry point, reaches this exact asset.
Difference Between Exposure Validation And Vulnerability Management?
The core difference is proof. Vulnerability management tells you a weakness exists and estimates how bad it could be. Exposure validation tests that weakness against your actual environment and tells you whether an attacker could use it today.
Where Vulnerability Management Stops?
- Relies on CVSS and theoretical severity
- Scans on a fixed schedule
- Treats each finding on its own
- Produces a long, growing backlog
Where Exposure Validation Picks Up?
- Tests real exploitability, not just presence
- Runs continuously or after every major change
- Chains findings the way an attacker would
- Produces a short list, proven and prioritized
Why Is Traditional Vulnerability Management No Longer Enough?
Traditional vulnerability management falls short because most published vulnerabilities are never exploited, yet scanners and CVSS scores treat many of them as urgent. Cyentia Institute’s EPSS research found that only about 6% of all published CVEs have ever been observed under exploitation activity in the wild, and even fewer ever spread beyond a small number of organizations.
Teams that patch by severity score alone spend most of their effort on the 94% that were never going to be used against them, while a handful of lower-scored findings sit exploitable because nothing forced anyone to test them. CISA’s Known Exploited Vulnerabilities catalog exists precisely because severity alone kept proving unreliable as a prioritization signal.
The attack surface itself has also outgrown periodic scanning. Every new cloud service, API, and third-party integration gives attackers more ground to search for the one path that works, and a point-in-time scan cannot keep pace with that rate of change. This is why attack surface analysis has become a standing requirement rather than a one-time project.
What Are The Benefits Of Exposure Validation?
- Cuts remediation noise: Teams patch what is provably reachable first, not everything CVSS marks as critical.
- Surfaces chained risk: Reveals attack paths that combine two or three medium findings into one critical route, something a single scan will not show.
- Builds governance clarity: Replaces a forty-page finding list with a short set of proven, exploitable paths that risk committees can act on.
- Strengthens audit and insurance conversations: Proof of tested resilience carries more weight with auditors, regulators, and cyber insurers than a scan report alone.
- Shortens the exposure window: Continuous validation, delivered through platforms such as Mirror, tests new code and configuration changes as they ship instead of waiting for the next quarterly assessment.
How Does Exposure Validation Fit Into A CTEM Program?
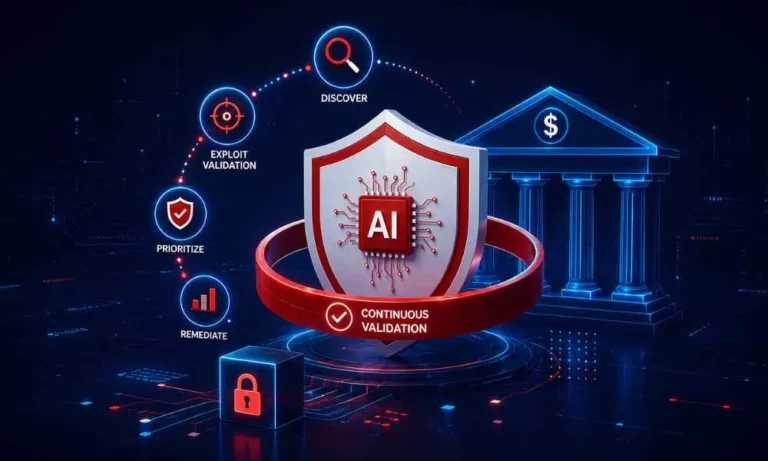
Gartner’s Continuous Threat Exposure Management framework places validation as one of five required stages: scoping, discovery, prioritization, validation, and mobilization. Validation is the stage most programs skip, and it is the one that decides whether the other four produce any real risk reduction. Gartner has projected that organizations prioritizing security investment through a continuous exposure management program will be three times less likely to suffer a breach by 2026.
Without validation, prioritization is a guess dressed up as a score. With it, security and governance leaders get a defensible answer to the question every board eventually asks: what can reach our critical assets. For a full walkthrough of the five stages, see our guide to CTEM.
What Are Best Practices For Combining Vulnerability Management And Exposure Validation?
- Keep vulnerability management as the wide net: Continue scanning broadly. It remains the fastest way to build a complete inventory of known weaknesses.
- Validate before you prioritize: Route critical and high findings through exploitability testing before locking a remediation order, not after.
- Test chains, not single findings: Ask what happens when a medium finding on one system meets a misconfiguration on another.
- Combine automated and expert-led validation: Continuous platforms catch drift between assessments; advanced penetration testing and red team assessment exercises catch what automation misses, including business logic flaws.
- Close the loop with mobilization: A validated finding with no owner and no deadline delivers no risk reduction. Assign it, track it, and confirm the fix closes the path.
- Report exploitability, not just counts: Give governance leaders and the board a short list of proven paths instead of a long list of theoretical ones.
Ready to know which of your vulnerabilities an attacker could use?
| Book a demo of Mirror, Ampcus Cyber’s AI-powered exposure validation platform. |
People Also Ask:
Is exposure validation the same as penetration testing?
No. Penetration testing is usually a scheduled, time-boxed engagement. Exposure validation borrows the same exploitation techniques but runs continuously or on a tighter cycle, testing new changes as they ship rather than once or twice a year.
How often should exposure validation be performed?
Critical and internet-facing assets should be validated continuously or after every significant change. Lower-risk internal assets can run on a monthly or quarterly cycle, aligned with your change management schedule.
Does exposure validation replace vulnerability management?
No. Vulnerability management still supplies the inventory of findings. Exposure validation decides which of those findings deserve immediate attention.
Who should own exposure validation in an organization?
It typically sits with the security operations or vulnerability management team, with governance and risk leaders using the validated output to set remediation priority and report risk to the board.
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.