



TL;DR
- NIST AI RMF is a voluntary risk method, ISO 42001 is a certifiable management system, and the EU AI Act is binding law with fines up to €35 million or 7% of global turnover.
- The Digital Omnibus moved Annex III high-risk obligations to December 2, 2027, but Article 50 transparency duties have applied since August 2, 2026.
- The three overlap heavily, so one integrated control framework with a documented crosswalk avoids running three separate programs.
Enterprise AI adoption has moved faster than most governance programs. Models now sit inside credit decisions, hiring pipelines, and third-party SaaS platforms, often before risk teams know who owns them. Boards, customers, and regulators now want proof that AI systems are safe, accountable, and lawful.
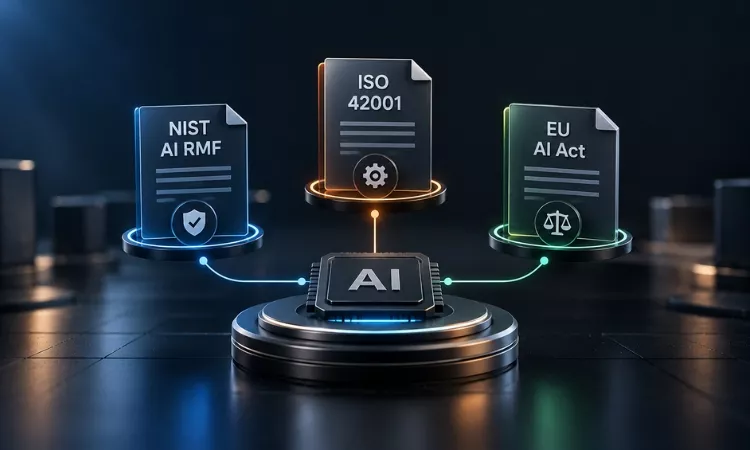
Comparing NIST AI RMF vs ISO 42001 vs the EU AI Act reveals three different instruments: a voluntary risk methodology, a certifiable management system standard, and a binding regulation. Leaders need to know what each requires, where they overlap, and how one program can satisfy all three.
NIST AI RMF vs ISO 42001 vs EU AI Act: What Is the Difference?
The NIST AI RMF is voluntary guidance for identifying and managing AI risk, ISO/IEC 42001 is an international standard for an auditable AI management system, and the EU AI Act is a law with financial penalties.
| Attribute | NIST AI RMF | ISO/IEC 42001 | EU AI Act |
| Type | Voluntary framework | Management system standard | Binding EU regulation |
| Current version | AI RMF 1.0 (2023) | ISO/IEC 42001:2023 | Regulation (EU) 2024/1689 |
| Certification | None | Yes, by accredited certification bodies | Conformity assessment for high-risk systems |
| Core structure | Govern, Map, Measure, Manage | Clauses 4 to 10 plus Annex A controls | Risk tiers: prohibited, high-risk, transparency, minimal |
| Cost of gaps | Operational and reputational risk | Audit nonconformities or lost certification | Fines up to €35 million or 7% of global annual turnover |
How Does the NIST AI Risk Management Framework Work?
The NIST AI RMF organizes AI risk management into four functions: Govern, Map, Measure, and Manage. Govern sets accountability, Map identifies system-specific risks, Measure analyses them, and Manage treats them.
The framework defines characteristics of trustworthy AI, such as safety, security, transparency, privacy, and managed bias. NIST supports it with a Playbook and the Generative AI Profile (NIST AI 600-1), published in July 2024.
As of October 2026, AI RMF 1.0 remains the current release, and NIST has stated it is being revised under the White House AI Action Plan. Teams can adopt it now and track the revision. Its main limitation is proof: with no certification, it cannot by itself demonstrate to customers or regulators that controls are operating.
What Does ISO 42001 Require for AI Governance?
ISO/IEC 42001 requires an organization to establish, implement, maintain, and continually improve an Artificial Intelligence Management System (AIMS), supported by a defined scope, AI policy, risk and impact assessments, controls, internal audit, and management review.
How ISO 42001 Is Structured?
- Clauses 4 to 10 follow the same harmonized structure as ISO 27001, from context and leadership to performance evaluation and improvement.
- Annex A provides 38 reference controls across nine objectives, from AI policy and impact assessment to data, lifecycle, and third-party relationships.
- AI system impact assessment evaluates consequences for individuals, groups, and society, and a Statement of Applicability records which controls apply.
Why ISO 42001 Certification Carries Weight?
Certification gives customers independent assurance, and since July 2025, ISO/IEC 42006 has set specific requirements for bodies that certify AI management systems. ISO 27001-certified organizations can extend existing document control, audit, and management review processes, which is why moving from ISO 27001 to ISO 42001 is often the fastest route to a functioning AIMS.
What Does the EU AI Act Require and When?
The EU AI Act classifies AI systems by risk and assigns legal obligations to providers and deployers, with the strictest requirements for high-risk systems. It also applies to non-EU organizations whose AI systems or outputs reach the EU market.
The application timeline is phased:
- February 2, 2025: Prohibited practices and AI literacy obligations.
- August 2, 2025: General-purpose AI model obligations.
- August 2, 2026: Article 50 transparency duties, including disclosure of AI interactions and labelling of deepfakes.
- December 2, 2027: Annex III high-risk systems (employment, creditworthiness, education), under the Digital Omnibus approved in June 2026.
- August 2, 2028: High-risk AI embedded in Annex I regulated products.
High-risk providers need risk management, data governance, technical documentation, logging, human oversight, cybersecurity controls, and a quality management system. Certain deployers must also complete a Fundamental Rights Impact Assessment. The deferral buys time, but documentation and data governance take long to build. Our EU AI Act compliance playbook for deployers covers these obligations in detail.
How Do the Three Frameworks Map to Each Other?
The three overlap heavily on governance, risk assessment, data quality, and human oversight, so one control set can generate evidence for all of them. They differ in legal force and in how compliance is proven.
| Governance area | NIST AI RMF | ISO/IEC 42001 | EU AI Act |
| Accountability | Govern | Clause 5, Annex A.3 | Article 17 (QMS), Article 26 (deployers) |
| Risk identification | Map | Clause 6.1, Annex A.5 | Article 9, Article 27 (FRIA) |
| Data quality | Map, Measure | Annex A.7 | Article 10 |
| Testing and monitoring | Measure | Clause 9, Annex A.6 | Article 15, Article 72 |
| Oversight and response | Manage | Clauses 8 and 10 | Article 14, Article 73 |
NIST AI RMF vs ISO 42001 in Practice
ISO 42001 is the operating model, NIST AI RMF is the risk method inside it, and the EU AI Act sets legal requirements on top. Note that ISO 42001 certification does not by itself create a presumption of conformity with the AI Act; that will come from harmonised European standards being developed by CEN and CENELEC. ISO 42001 evidence remains highly reusable.
Which AI Governance Framework Should Your Organization Prioritize?
Prioritize by legal obligation first, market assurance second, and risk methodology third. The AI Act is mandatory if your AI reaches the EU market, ISO 42001 matters when customers want independent proof, and NIST AI RMF works as an internal method anywhere.
Three hypothetical profiles illustrate this:
- A US SaaS provider selling AI features will likely face ISO 42001 requests in security questionnaires, with NIST AI RMF shaping internal risk work.
- A lender scoring EU applicants runs an Annex III high-risk system and needs AI Act conformity, with ISO 42001 as the management system underneath.
- An ISO 27001-certified enterprise can extend its ISMS into an AIMS and map controls to both NIST and the AI Act.
Where Do AI Governance Programs Commonly Fall Short?
Most gaps come from incomplete AI inventories, policies without operating evidence, and unclear ownership:
- No complete inventory covering shadow AI and AI embedded in vendor products
- Confusion over provider versus deployer roles under the AI Act
- Limited visibility into third-party models, which a structured AI vendor due diligence questionnaire helps address
- Three parallel programs producing duplicate evidence, and December 2027 treated as a start date
What Should Organizations Do Next?
Start with an AI inventory and applicability assessment, then build one integrated control framework that maps to all three requirements.
- Inventory AI systems and classify each by AI Act risk tier and role.
- Assign accountability through a governance committee and named owners.
- Run a gap assessment against ISO 42001 clauses and Annex A, using NIST functions as the risk method.
- Build a unified control library with a documented crosswalk.
- Operationalize evidence such as impact assessments, model documentation, and monitoring logs.
- Set a certification and conformity roadmap supported by internal audit.
Teams can benchmark their starting point with the four stages of AI governance maturity. Where internal capacity is limited, Ampcus Cyber’s ISO 42001 and AI governance services help teams assess gaps, design the AIMS, and prepare evidence that serves both certification auditors and EU AI Act obligations.
Building One Program Across NIST AI RMF, ISO 42001, and the EU AI Act
The NIST AI RMF vs ISO 42001 vs EU AI Act decision is ultimately a sequencing exercise. The AI Act sets the legal floor, ISO 42001 makes governance auditable, and NIST AI RMF sharpens risk analysis. Organizations that build one integrated control framework now will reach the December 2027 deadline with evidence already in place.
| Know exactly where your AI systems stand against all three frameworks. Schedule your AI governance assessment with our experts. |
People Also Ask
Is ISO 42001 mandatory under the EU AI Act?
No. ISO 42001 is a voluntary standard. It helps organizations build the risk management, documentation, and oversight the AI Act expects, but certification does not by itself prove AI Act conformity.
Does the EU AI Act apply to US companies?
Yes, when a US company places an AI system on the EU market or when the system’s outputs are used in the EU. Location of headquarters does not determine applicability.
Can NIST AI RMF be used for EU AI Act compliance?
Partially. NIST AI RMF provides a strong method for identifying and measuring AI risk, but it does not cover AI Act specifics such as conformity assessment, CE marking, EU database registration, or serious incident reporting.
Do we need ISO 42001 if we already have ISO 27001?
ISO 27001 protects information security but does not address AI-specific risks such as bias, model drift, or societal impact. ISO 42001 adds those controls and shares the same clause structure, so the extension is efficient.
Has the EU AI Act high-risk deadline been delayed?
Yes. The Digital Omnibus moved Annex III high-risk obligations to December 2, 2027, and Annex I product-embedded systems to August 2, 2028. Article 50 transparency duties still applied from August 2, 2026.
Is there a NIST AI RMF 2.0?
Not yet. As of October 2026, AI RMF 1.0 is the current version, and NIST has announced a revision under the White House AI Action Plan without publishing a new draft.
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.