



Enterprises now use AI for credit decisions, hiring screens, fraud alerts, customer service and internal code generation. Most adopted these tools faster than they defined who approves them, who monitors them and who answers when they fail.
A 2026 ISACA AI Pulse Poll preview found that organizations are deploying AI faster than they can govern it. Regulators are responding. India’s Ministry of Electronics and Information Technology released AI Governance Guidelines in November 2025, and the EU AI Act sets risk-tiered obligations.
This article explains what AI governance covers, which frameworks apply, which roles the program needs and how to run it as a repeatable operating model.
What Is AI Governance?
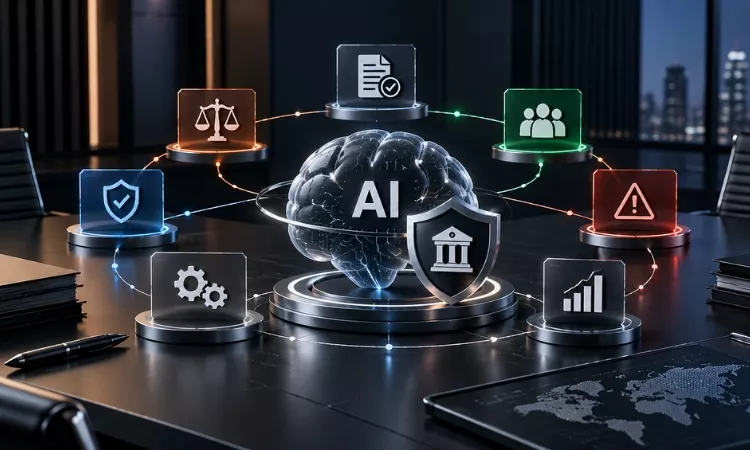
AI governance is the discipline that decides who may approve an AI system, what evidence it must produce first and who answers when it fails. It covers the full lifecycle, from intake through retirement. Every model, dataset and vendor tool needs a named owner, or accountability depends on individual judgment.
AI ethics states principles such as fairness, transparency and accountability. Governance turns those principles into enforceable controls, approval workflows and evidence. A principle without an owner, a control and a record will not hold up under a regulator’s questions or a board inquiry. Programs that need help designing this structure can start with governance framework development.
Why Does AI Governance Matter Now?
Three pressures make governance a board-level issue;
The first is regulation. Under the EU AI Act, obligations for general-purpose AI models have applied since 2 August 2025. The EU Digital Omnibus moved high-risk obligations for standalone Annex III systems to 2 December 2027 and for product-embedded Annex I systems to 2 August 2028. Confirm the final dates in the Official Journal before setting internal deadlines.
The second pressure is India’s policy approach. The MeitY guidelines do not create a separate AI law. They rely on existing legislation, including the Digital Personal Data Protection Act, 2023, and organize the approach around seven principles, with oversight shared across sectoral regulators. The official guidelines are published by the Ministry of Electronics and Information Technology.
The third pressure is operational. AI agents that call tools and access systems create exposure that traditional application controls do not address.
Which Frameworks Should Govern Enterprise AI?
The NIST AI Risk Management Framework (AI RMF 1.0), published in January 2023, is a voluntary framework built on four functions: Govern, Map, Measure and Manage. Govern runs across the other three and keeps them repeatable. The framework is published by the National Institute of Standards and Technology. ISO/IEC 42001:2023 is a certifiable AI management system standard. Binding regulations such as the EU AI Act define legal obligations for specific markets. Most organizations pair one operating framework with the regulations that apply to them.
| Framework | Type | Primary Use | Where It Fits in the Program |
| NIST AI RMF 1.0 | Voluntary risk framework, no certification | Shared risk vocabulary and four functions | Risk identification and control design |
| ISO/IEC 42001:2023 | Voluntary, certifiable management system | Policies, roles, continual improvement and audit | Operating model and third-party assurance |
| EU AI Act (Regulation (EU) 2024/1689) | Binding regulation | Risk tiers, prohibited practices, high-risk duties | Compliance for systems serving EU users |
| MeitY India AI Governance Guidelines (2025) | Policy guidance | Seven principles, risk assessment, institutional oversight | Indian operations and sectoral regulator expectations |
| ISO/IEC 27001 and NIST CSF | Security standards | Controls for AI infrastructure, data and access | Security baseline beneath AI controls |
ISO/IEC 42001 defines how the program runs. NIST AI RMF gives technical teams the risk language they use daily. Neither replaces the EU AI Act, and ISO/IEC 42001 is not currently a harmonized standard under that regulation. Teams preparing for ISO/IEC 42001 can review the PECB ISO/IEC 42001 certification pathway.
Who Is Responsible For AI Governance Inside An Enterprise?
Ownership remains unsettled. In the ISACA AI Pulse Poll 2026 preview, 28% of respondents said the board or executives would be responsible if an AI system caused serious harm, 18% pointed to the CIO or CTO, 13% pointed to the CISO and 20% did not know. The Splunk CISO Report 2026, which surveyed 650 CISOs, found that 96% now carry responsibility for AI governance and risk management. A Gartner poll from June 2024 found that 55% of organizations had an AI board, and that 88% of organizations with an AI leader did not give that person the title of Chief AI Officer.
The practical answer is a shared model with clear decision rights:
- Board risk committee: Approves AI risk appetite and receives periodic reporting on high-risk systems.
- AI governance committee: Chaired by the CISO or an accountable executive, it approves high-risk use cases and resolves cross-functional conflicts.
- Accountable AI executive: Owns the AI use policy and system inventory. This may be a Chief AI Officer or an existing executive with a defined mandate.
- Model owners: Accountable within each business unit for performance, drift and documentation.
- Data stewards: Confirm provenance, lawful basis, retention and purpose limitation, including alignment with DPDPA consent requirements.
- CISO and security architecture: Set access controls, logging, adversarial testing and AI supply chain review.
- Legal, privacy and compliance: Map obligations across the EU AI Act, the DPDPA and sectoral rules.
- Internal audit: Tests controls independently against the chosen framework.
Ready to build an AI governance operating model your board can audit?
| Contact the Ampcus Cyber team for an AI governance readiness review. |
People Also Ask
What Is the Difference Between AI Ethics and AI Governance?
AI ethics defines the principles an organization values, such as fairness and transparency. AI governance turns those principles into owned processes, controls and records. Ethics states the intent, and governance produces the proof.
Is ISO/IEC 42001 Certification Mandatory?
No. ISO/IEC 42001 is voluntary, and no country currently requires certification by law. Accredited third-party bodies certify the management system, not ISO itself. Certification does not make an AI system compliant with the EU AI Act, because the standard is not harmonized under that regulation. The International Organization for Standardization publishes the standard.
What Is The NIST AI RMF?
The NIST AI Risk Management Framework is voluntary guidance published in January 2023. It organizes AI risk work into Govern, Map, Measure and Manage. It is a risk framework, not a certification scheme.
Does India Have A Law That Regulates AI?
Not a standalone AI statute. The MeitY AI Governance Guidelines, released on 5 November 2025, rely on existing laws, sectoral regulators and voluntary measures. Enterprises processing personal data for AI training or inference must still meet DPDPA obligations.
Who Should Own AI Governance In An Enterprise?
Ownership works best when an executive sponsor is accountable for the program and a governance committee makes the decisions. Day-to-day responsibility sits with model owners and data stewards in each business unit. Survey results show that many organizations have not yet assigned this accountability clearly.
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.