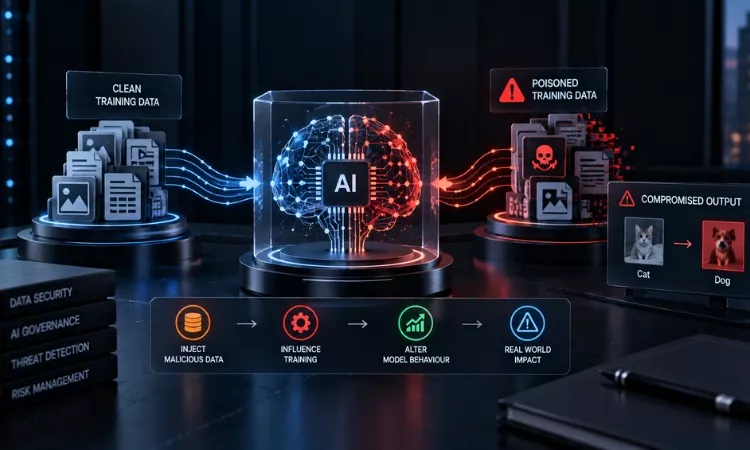
This infographic explores the cybersecurity risks emerging as AI agents gain the ability to act autonomously, make decisions, access data, and interact with business systems. Unlike traditional AI applications, agentic AI can execute tasks through connected tools, APIs, applications, and other agents, creating a broader and more dynamic attack surface.
It highlights eight critical agentic AI security risks: prompt injection, excessive agency, tool abuse, data exposure, identity and privilege abuse, agent-to-agent attacks, memory poisoning, and supply chain risk. Each risk is explained in concise, practical language to help security leaders, governance teams, technology executives, and organizations understand where autonomous AI systems may introduce new vulnerabilities.
The infographic is designed to support AI security, AI governance, agentic AI risk management, cybersecurity strategy, and responsible AI adoption. It provides a useful reference for organizations evaluating AI agents across enterprise environments in India, the United States, Europe, the Middle East, and other global markets.
For organizations asking “What are the security risks of agentic AI?”, “How can AI agents be attacked?”, or “How should enterprises secure autonomous AI systems?”, this visual provides a clear starting point for understanding the threat landscape and the controls needed as AI autonomy expands.
Enjoyed reading this infographics? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.