Cloud adoption is no longer an experiment. Most enterprises run production workloads across two or three public cloud providers, supported by SaaS platforms, container clusters and third-party APIs that change every week. That speed creates a visibility problem.
Configuration drift, over-privileged identities and unmanaged storage buckets appear faster than governance teams can review them. Auditors and regulators have noticed. A structured cloud security assessment gives leadership a dated, evidence-based view of where these exposures sit and which ones carry the most liability.
What Does a Cloud Security Assessment Include?
A cloud security assessment is a structured review of a cloud environment against defined security controls, threat scenarios and compliance requirements. It examines how workloads are configured, who can access them, how data is protected and how the organization detects and responds to incidents. The output is a prioritized register of findings with risk ratings and remediation guidance.
Why Do Enterprises Need a Cloud Security Assessment
Enterprises need one because the shared responsibility model places configuration and identity duties on the customer, even though the provider secures the underlying infrastructure. A public storage bucket or an access key that was never rotated remains the customer’s exposure. An assessment converts that responsibility into a documented position that boards, auditors and regulators can review.
Three triggers usually start the work:
- Regulatory obligations under PCI DSS v4.0, HIPAA or ISO/IEC 27001:2022 that require documented cloud controls.
- Board questions about concentration risk after a peer incident.
- Mergers, new cloud regions or migrations that change the data flow map.
Quick Answer: What Is the Main Purpose?
A cloud security assessment verifies that cloud configurations, identities and data controls match the organization’s security policy and regulatory obligations. It identifies gaps before attackers or auditors find them, and it produces evidence that supports risk acceptance decisions. Most assessments also feed a remediation roadmap tied to business priorities.
What Is the Scope of a Cloud Security Assessment?
Scope defines which accounts, subscriptions, workloads, identities and data stores fall inside the review. Scope decisions drive cost, timeline and the credibility of the final report. A narrow scope misses lateral movement between environments, while an overly broad scope stalls delivery. Agree on the boundary before any testing begins.
| Scope Domain | Typical Coverage | Example Control Checked |
| Identity and access | IAM roles, MFA, privileged accounts | Root account MFA enforced |
| Network | VPC routing, security groups, WAF | No unrestricted inbound access to admin ports |
| Data protection | Encryption at rest and in transit, key management | Key rotation enabled on customer-managed keys |
| Workloads | Containers, virtual machines, serverless functions | Image scanning before deployment |
| Logging and monitoring | Audit trails, SIEM integration | Audit logs retained for 365 days |
| Third-party and SaaS | Integrations, OAuth grants, vendor access | Stale OAuth tokens revoked |
How Does a Cloud Security Assessment Work Step by Step?
A cloud security assessment runs in five phases: scoping, discovery, control testing, risk analysis and reporting. Each phase produces artifacts the next phase depends on, so skipping discovery weakens every finding that follows.
- Scoping and rules of engagement: Confirm business owners, cloud accounts, compliance drivers and testing boundaries. Define what the assessor may and may not touch.
- Discovery and asset inventory: Export configuration snapshots, IAM policies and network topology. Reconcile them against the CMDB, because shadow accounts usually surface here.
- Control testing: Compare configurations against CIS Benchmarks and the Cloud Security Alliance Cloud Controls Matrix baseline. Validate exploitable paths, not only settings.
- Risk analysis: Rate findings by exploitability, data sensitivity and exposure. A public bucket holding cardholder data outranks a missing resource tag.
- Reporting and remediation planning. Deliver findings with named owners, target dates and retest criteria.
Which Compliance Frameworks Does a Cloud Security Assessment Support?
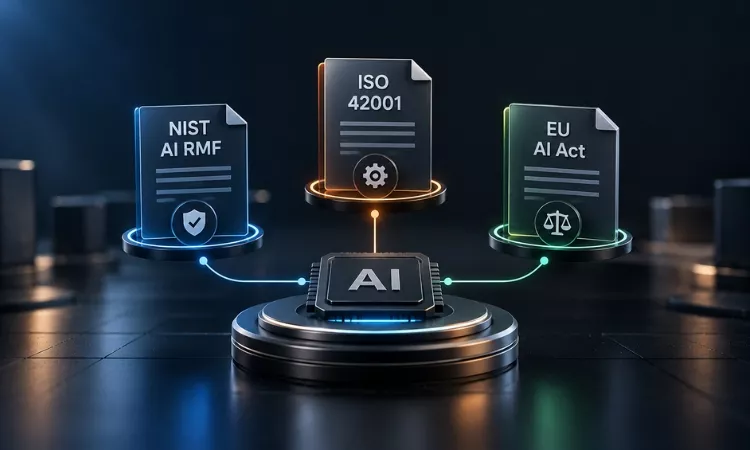
A cloud security assessment supports PCI DSS v4.0 requirements for cardholder data environments, HIPAA Security Rule safeguards for electronic protected health information, ISO/IEC 27001:2022 Annex A controls, SOC 2 Trust Services Criteria and the NIST Cybersecurity Framework 2.0. For AI workloads, evidence can map to the NIST AI Risk Management Framework (AI RMF 1.0). One well-scoped assessment often produces evidence for several of these at once, which reduces duplicate audit effort. Where penetration testing is part of the engagement, PCI SSC guidance and CREST-accredited testers add independent credibility to the results.
Ampcus Cyber maps findings to controls through Compliance Compass, so each gap appears against the specific clause it affects.
What Deliverables Should a CISO Expect from a Cloud Security Assessment?
A CISO should expect an executive summary, technical findings register, an evidence package and a remediation roadmap. Each deliverable serves a different reader, so the report should separate board-level risk language from engineering detail. A report that mixes both usually fails in both rooms.
- An executive summary with an overall risk posture rating and the top five exposures stated in business terms.
- Findings register listing each issue, affected asset, severity and mapped control.
- An evidence package with configuration exports and screenshots retained for audit.
- A remediation roadmap sorted by exposure and effort, with named owners.
- A retest report confirming closure of each finding.
How Often Should Organizations Run a Cloud Security Assessment?
Organizations should run a full cloud security assessment annually and targeted reviews after material changes. The annual cycle aligns with most audit calendars. Targeted reviews follow new cloud regions, acquisitions, identity platform changes or a new payment flow. Continuous posture monitoring covers the gap between formal assessments, but it does not replace the human review of attack paths and business context.
| Ready to define your cloud scope before the next audit cycle? Contact Ampcus Cyber to book a scoping session with our cloud security team. |
People Also Ask
How long does a cloud security assessment take?
A focused assessment of one cloud account typically takes two to four weeks. Multi-account enterprise environments with regulated workloads often need six to ten weeks, depending on scope and access approvals.
Is a cloud security assessment the same as a penetration test?
No. An assessment reviews configuration, identity and governance against defined controls. A penetration test attempts to exploit weaknesses. Many programs combine both, with penetration testing scoped as a component of the assessment.
Who should own the assessment inside the organization?
The CISO or security governance lead should own the assessment, with cloud platform owners accountable for remediation. Internal audit should receive the final report for independent review.
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.