A compliance director at a mid-sized asset management firm in Frankfurt spent three weeks preparing her annual third-party risk report. Her Register of Information listed 214 ICT vendors, including providers supporting cloud hosting, trade settlement, market data, and portfolio analytics.
She assumed vendor questionnaires and SOC 2 reports covered her DORA obligations. Then her cloud provider appeared on the European Supervisory Authorities’ first roster of Critical ICT Third-Party Providers.
The vendor she reviewed annually was now under direct EU regulatory oversight. Her own due diligence obligations remained, but a new oversight layer had emerged.
This is the reality for risk and compliance teams across the EU financial sector. Here’s what Critical ICT Third-Party Provider designation means, who determines it, and what it changes for financial entities relying on these providers.
What Is A Critical ICT Third-Party Provider Under DORA?
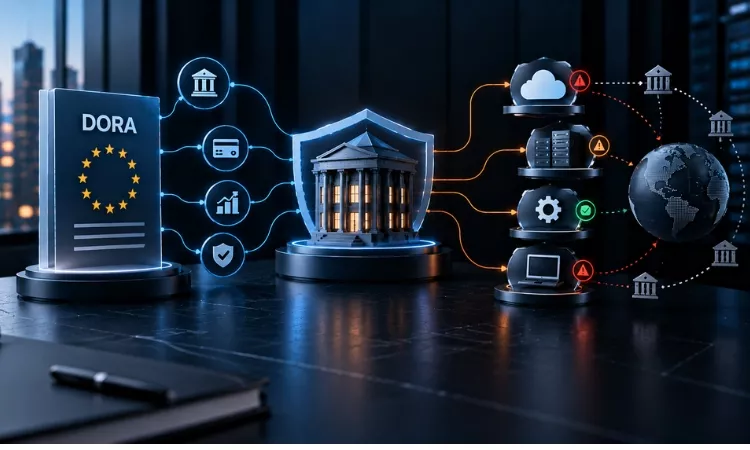
A Critical ICT Third-Party Provider, or CTPP, is an information and communication technology vendor that the European Supervisory Authorities have formally designated as systemically important to the EU financial sector under the Digital Operational Resilience Act. Regulation (EU) 2022/2554 created this designation as part of its Oversight Framework, set out in Articles 31 through 44. The framework covers ICT vendors such as cloud platforms, data centre operators, and core infrastructure providers, whose services touch a large enough share of the financial sector that their failure could ripple across multiple banks, insurers, and investment firms at once.
Not every vendor a financial entity uses qualifies. DORA separates standard ICT third-party providers, who remain the direct responsibility of the financial entities using them, from CTPPs, who face added EU-level supervision on top of that. A cloud provider hosting one mid-sized bank’s systems is unlikely to meet the bar. A provider hosting core infrastructure for hundreds of banks across a dozen member states is a different story.
How Do The ESAs Decide Which Providers Get Designated As Critical?
The European Banking Authority, European Securities and Markets Authority, and European Insurance and Occupational Pensions Authority jointly run the designation process. The assessment starts with the Registers of Information that every financial entity in scope of DORA must maintain, documenting each ICT contractual arrangement in detail.
The ESAs pull data from these registers and run providers through a two-step methodology. The first step applies six quantitative thresholds covering factors such as how many financial entities depend on the provider and how much of the sector’s assets those entities represent. Providers that clear this step move to a second round of five qualitative sub-criteria, examining substitutability, the provider’s role in critical or important functions, and its overall systemic footprint. Eleven sub-criteria in total feed into a single designation decision.
Providers flagged as potentially critical receive formal notice and a window to respond before any designation becomes final. This right to be heard gives vendors a chance to submit a reasoned statement challenging the assessment before the ESAs issue their decision.
Who Are The First Companies Designated As CTPPs?
The ESAs published their first list of designated CTPPs on 18 November 2025, under Article 31(9) of DORA. Nineteen providers made the initial list, spanning cloud infrastructure, data centre operations, telecommunications, and financial data and software services. Large hyperscale cloud platforms feature prominently, reflecting how concentrated EU financial institutions have become around a few infrastructure providers.
This first list will not be the last. The ESAs are expected to expand the roster as more Register of Information data arrives and new services reach systemic scale. Treat the current list as a floor, not a fixed count, and revisit vendor risk on a rolling basis rather than once a year.
What Changes Once A Provider Is Designated As A CTPP?
Designation triggers direct EU-level oversight instead of oversight left entirely to national regulators. Each CTPP is assigned a Lead Overseer, one of the three ESAs, who takes on responsibility for ongoing supervision. The Lead Overseer reviews whether the provider has sound governance and risk management in place, covering service security and availability, incident identification and reporting, systems testing, and the data portability arrangements that let financial entities exit if needed.
The Lead Overseer can request information, run inspections, and issue recommendations directly to the CTPP. It cannot impose fines or binding orders on its own. Enforcement runs through a second layer: if a CTPP does not address a serious and persisting risk, national competent authorities can require the financial entities using it to suspend, phase out, or terminate the specific services involved. Pressure lands on the provider first and only reaches dependent financial entities if the risk stays unresolved.
Does CTPP Designation Reduce A Financial Entity’s Own Third-Party Risk Duties?
No, and this is the point compliance teams miss most often. CTPP designation adds a supervisory layer at the EU level. It does not transfer a financial entity’s own due diligence, contract management, and monitoring obligations to the ESAs.
Every financial entity in scope of DORA still has to maintain its Register of Information for all ICT vendors, classify which ones support critical or important functions, negotiate contracts with audit rights and exit provisions, and assess concentration risk across its full vendor portfolio. A vendor’s CTPP status is useful context for that risk work. It signals that the provider now faces external scrutiny and structured incident reporting requirements. It does not substitute for the entity’s own ongoing vendor monitoring or its assessment of how far a single vendor failure could spread.
Firms still relying on annual questionnaires and static risk scores are already behind. Continuous, AI-driven third-party risk platforms close that gap by tracking vendor risk signals, contract obligations, and concentration exposure in real time, since a vendor’s regulatory profile can now shift with a single ESA designation.
What Should Compliance And Security Teams Do Now?
Start by cross-referencing your Register of Information against the published CTPP list to flag any vendor now under direct ESA oversight. Review the contracts tied to those vendors for exit and substitutability provisions, since portability is one of the areas Lead Overseers examine closely. Reassess concentration risk across your cloud and infrastructure vendors as a group, since DORA’s entire rationale rests on systemic dependency rather than single-vendor failure.
Build a recurring cadence instead of treating this as a one-time exercise. The list will grow, vendor risk profiles will shift, and a structured third-party risk management program keeps that work manageable. Teams still running vendor risk through spreadsheets should look at how modern TPRM programs use risk scoring and automation to keep pace with a regulator that now updates its own critical vendor list instead of waiting for the next audit cycle.
Cloud concentration and vendor dependency are not going away, and DORA’s CTPP framework is only the first EU-level attempt to supervise that risk directly.
| Talk to Ampcus Cyber about aligning your third-party risk program with DORA’s oversight framework before your next audit cycle. |
People Also Ask
Is DORA only relevant to companies headquartered in the EU?
What is the difference between a CTPP and a regular ICT vendor under DORA?
Can the list of designated CTPPs change?
Who pays for CTPP oversight?
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.