TL;DR
- 13 November 2026: Rule 4 goes live, allowing eligible entities (₹2 crore minimum net worth) to register as official Consent Managers with the DPBI.
- No Direct Penalty Yet: Substantive obligations for Data Fiduciaries (itemized notices, mandatory withdrawal handling, security controls) apply from 13 May 2027.
- Interoperability is Mandatory: You don’t have to hire a Consent Manager, but your systems must be ready to receive and honor consent and withdrawal requests sent through one.
- Architectural Gap: Fiduciaries must automate consent APIs to propagate withdrawals across downstream databases, SaaS tools, and data processors to avoid penalties of up to ₹250 crore.
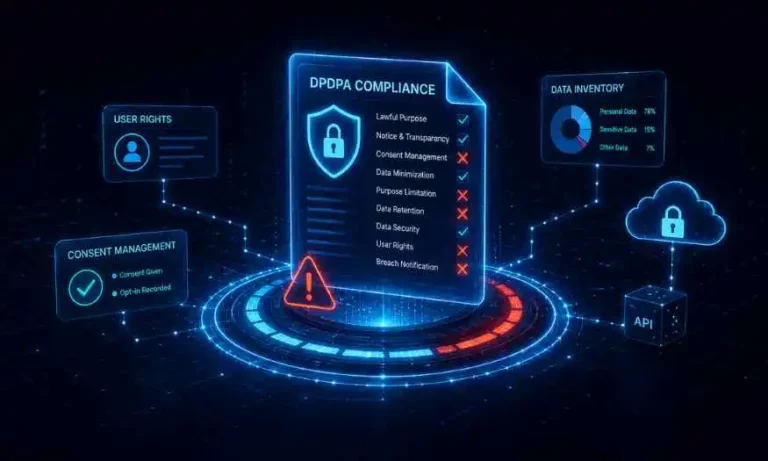
India’s Digital Personal Data Protection Act, 2023 changes how organisations collect, record, and honour consent, and the DPDP Rules, 2025 introduce a new intermediary into that flow.
On 13 November 2026, Rule 4 comes into force and opens the registration route for Consent Managers, entities that let individuals give, review, and withdraw consent across services through a single interface. For Data Fiduciaries, the organisations that decide why and how personal data is processed, the date creates no direct penalty exposure. It does raise a practical question: can consent systems built around a single application accept, record, and act on instructions that arrive from an external platform? Answering that before substantive obligations begin on 13 May 2027 is far easier than doing it after enforcement starts.
What Happens on 13 November 2026 Under the DPDP Rules?
Rule 4 of the DPDP Rules, 2025 comes into force on 13 November 2026, one year after the Rules were notified, and it opens registration with the Data Protection Board of India for entities that want to operate as Consent Managers. The date places no new obligation on an ordinary Data Fiduciary. The wider provisions on notice, security, breach reporting, and related duties come into force on 13 May 2027, which is the date a DPDPA readiness roadmap should be built around.
MeitY consulted on shortening some timelines in January 2026, with a focus on Significant Data Fiduciaries. That proposal had not been confirmed as gazetted in recent coverage, so organisations should plan for 13 May 2027 while watching for official amendments.
Who Can Register as a Consent Manager?
Registration is open to eligible Indian companies that meet the conditions in the Rules. Under the First Schedule, a company needs a minimum net worth of ₹2 crore. That threshold applies to Consent Managers only and does not decide whether the Act applies to an ordinary business.
What Is a Consent Manager and How Does It Work for Data Fiduciaries?
A Consent Manager is a registered intermediary that lets a Data Principal, the individual whose data is processed, give, manage, review, and withdraw consent through a single accessible platform. It acts on behalf of the individual and is accountable to them, not to the fiduciary.
| Party | Role in the Consent Flow |
| Data Principal | Gives, reviews, and withdraws consent. |
| Consent Manager | Registered intermediary that records and relays consent actions. |
| Data Fiduciary | Determines purposes, honours consent decisions, and remains accountable. |
| Data Processor | Processes data for the fiduciary and must act on withdrawals. |
| Data Protection Board | Registers Consent Managers and adjudicates breaches. |
For fiduciaries, the shift is architectural. Consent that once lived inside one application’s database may now be changed from an outside platform, and the fiduciary must respond reliably.
Do Data Fiduciaries Have to Use a Consent Manager?
No. Rule 4 sets up registration for Consent Managers and does not oblige ordinary fiduciaries to route consent through one. This is one of the common myths about the DPDP Rules, since in-house systems and other suitable approaches can also support compliance. The Act gives Data Principals the option to use a Consent Manager, so fiduciaries should expect individuals to exercise it and be ready to honour those instructions. Confirm the position against the Act and any sector-specific guidance before finalising your design.
Why Does Consent Manager Readiness Matter Before May 2027?
Readiness matters because withdrawal, notice, and security duties apply from 13 May 2027, and integration work touches systems with long lead times. The Act requires withdrawal to be as easy as giving consent, and once consent is withdrawn the fiduciary must cease processing, and cause its processors to cease, within a reasonable time.
Those duties are hard to meet with manual processes. A withdrawal arriving through an external platform must reach marketing tools, analytics pipelines, data warehouses, and processors. Consent artefacts are also personal data, and failure to maintain reasonable security safeguards can attract penalties of up to ₹250 crore under the Act’s Schedule.
How Should Data Fiduciaries Prepare for Consent Manager Integration?
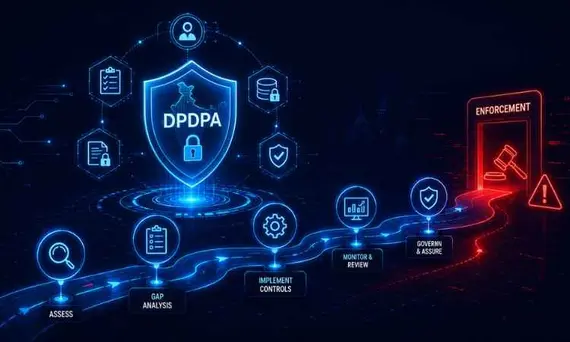
Fiduciaries should prepare by mapping purposes to systems, building a reliable consent record, and testing withdrawal end to end. A practical sequence:
- Inventory processing purposes and map each to its consent basis, data stores, and processors. Uncontrolled data sprawl across cloud and SaaS tools is a common reason this step takes longer than planned.
- Review notices for clear, itemised purposes and accessible language.
- Design a consent record store that captures purpose, timestamp, version, and source channel.
- Build withdrawal propagation to downstream systems and processors, with defined response times. Vendors are where deletion and withdrawal often break, so review third-party data risk in your processor contracts.
- Define secure APIs for inbound consent events, with authentication, logging, and monitoring.
- Assess any Consent Manager partner for registration status, security posture, audit reports, and contractual responsibilities.
- Test end to end, including a tabletop exercise on a high-volume withdrawal.
Confirm technical interoperability details once the Board and MeitY publish them.
What Are the Common Gaps in Consent Architecture?
The most common gaps are coarse consent records, manual withdrawal handling, and weak visibility into processors. Typical examples include:
- A single checkbox covering several purposes, which makes purpose-level withdrawal impossible.
- Withdrawal handled through an email inbox with no tracking or deadline.
- Processors and SDKs that continue to receive data after consent changes.
- Copies of personal data in legacy systems that withdrawal workflows never reach.
- No audit trail showing what the individual was told and when they agreed.
- Unclear handling of verifiable consent for children’s data.
What Should Organizations Do Next?
Organizations should run a consent readiness assessment now, while integration work still fits comfortably before May 2027. Start with a data and purpose map, test withdrawal against real systems, and rank gaps by risk. A quick baseline is available through Ampcus Cyber’s DPDPA self-assessment tool, which covers consent, security, breach management, and governance.
If the review exposes weaknesses, an independent assessment can validate consent architecture, check security safeguards around consent records, and review processor risk. Ampcus Cyber supports this through its Digital Personal Data Protection Act compliance services, which help teams turn legal requirements into testable controls and audit-ready evidence.
Using the Window Between November 2026 and May 2027
The November date introduces a new participant in consent flows without creating a new deadline for most fiduciaries. The deadline that matters is May 2027. Organizations that map purposes, build dependable consent records, and test withdrawal now will meet that date with evidence in hand and room to adapt if the rules change.
| Test your consent architecture before enforcement begins. Speak with Ampcus Cyber about a DPDP consent readiness assessment. |
People Also Ask:
What is a Consent Manager under the DPDP Act?
Is it mandatory for Data Fiduciaries to use a Consent Manager?
When will Consent Manager registration begin under the DPDP Rules?
Who can become a registered Consent Manager under the DPDP Rules?
What happens when a Data Principal withdraws consent under the DPDP Act?
Enjoyed reading this blog? Stay updated with our latest exclusive content by following us on Twitter and LinkedIn.